Live CISM Exam Preparation for Australian Security Professionals
EduDelphi combines practitioner-led teaching, a structured LMS, 3,000+ practice and revision resources, multiple mock exams, recordings and direct support in one connected CISM preparation route.
- Prepare for the CISM outline applying on your booked exam date.
- Build management-level judgement across governance, risk, security programs and incidents.
- Choose live online, classroom, private, hybrid, weekend or corporate delivery.
CISM Course Fees, Next Batch & What Is Included
Choose the delivery route that fits your work schedule. EduDelphi tuition covers the guided preparation experience; official ISACA costs remain separate and transparent.
Live delivery
Join instructor-led online or classroom preparation, with private and corporate routes also available.
Australia-compatible schedule
Daytime, evening and weekend options support professionals across Australian time zones.
Complete preparation
Live teaching, recordings, LMS resources, domain practice, multiple mocks and revision support.
Enquiry-led tuition
Request the current AUD fee, available batch formats and a preparation recommendation for your target date.
Which CISM Syllabus Applies to Your Exam Date?
Candidates testing up to 2 November 2026 use the earlier outline. Candidates testing from 3 November 2026 use the revised outline. EduDelphi’s teaching, resources and revision support are fully updated for both routes.
Exam up to 2 November 2026
| Domain | Weight |
|---|---|
| Information Security Governance | 17% |
| Information Security Risk Management | 20% |
| Information Security Program | 33% |
| Incident Management | 30% |
Exam from 3 November 2026
| Domain | Weight |
|---|---|
| Information Security Governance | 18% |
| Information Security Risk Management | 20% |
| Information Security Program | 33% |
| Incident Management | 29% |
Official reference: ISACA CISM Exam Content Outline.
What Is CISM Certification and Who Issues It?
CISM is a management-focused information-security credential. It is designed for professionals who govern security, manage risk, lead security programs and oversee incident readiness and response.
ISACA
Sets the examination, evaluates certification applications and governs ongoing maintenance requirements.
CISM
The Certified Information Security Manager credential awarded to candidates who meet the exam, experience, application and ethics requirements.
EduDelphi
Provides independent CISM training, exam preparation, practice, mocks and candidate support. EduDelphi does not issue the certification.
Why Choose EduDelphi for CISM Exam Preparation?
CISM rewards management judgement—not technical memorisation. Every part of the EduDelphi learning system is built to help candidates understand the decision behind the scenario.
Practitioner-led CISM teaching
Learn with Kashif Akhtar, a CISM, CISA, CRISC and CDPSE-qualified trainer with 30+ years across technology, cybersecurity, governance and enterprise risk.
40+ guided hours
Build the four domains systematically through live explanation, scenario reasoning and exam-focused review.
A structured CISM LMS
Keep recordings, learning resources, question practice, mock exams and revision materials organised in one place.
3,000+ resources
Move from domain-level knowledge checks to integrated management scenarios and final revision.
Multiple timed mocks
Practise pace, stamina, prioritisation and elimination while identifying weaker domains before exam day.
Human support
Use doubt solving, recordings, study planning and trainer feedback to stay consistent around demanding work schedules.
What Is Included in EduDelphi CISM Training?
The course connects teaching, practice and revision instead of leaving candidates to assemble a study route from unrelated materials.
| Learning component | How it supports your preparation |
|---|---|
| Live instructor-led classes | Build domain knowledge and management-level reasoning with direct explanation. |
| Full LMS and recording access | Revisit lessons and keep preparation organised around work and travel. |
| 3,000+ practice and revision resources | Strengthen recall, interpretation, prioritisation and cross-domain judgement. |
| Multiple mock examinations | Practise full-exam pacing and identify domains requiring final revision. |
| Revision notes and learning assets | Consolidate high-value concepts before the examination. |
| Doubt solving and trainer support | Understand why an answer is right and why plausible alternatives are weaker. |
| Official-process guidance | Understand ISACA registration, PSI scheduling and certification-application steps. |
| Flexible delivery | Choose live online, classroom, private, hybrid, evening, weekend or corporate formats. |
Who Should Take CISM Training in Australia?
Security professionals
Cybersecurity and information-security practitioners moving toward governance, program or management responsibility.
Security managers
Current managers and CISO-track professionals strengthening enterprise-level decision making.
Risk and GRC professionals
Technology-risk, cyber-risk, compliance and governance professionals working across business and security teams.
IT auditors and CISA holders
Assurance professionals moving from evaluating controls toward managing security strategy and programs.
IT and technology managers
Leaders responsible for security governance, third parties, resilience or incident oversight.
Consultants and advisers
Professionals helping organisations improve security governance, risk decisions and management reporting.
CISM Syllabus 2026: Four Information Security Management Domains
The course follows the official four-domain structure and teaches how governance, risk, program leadership and incident management influence one another.
Domain 1: Information Security Governance
Connect enterprise objectives with information-security strategy, accountability and oversight.
- Organisational strategy, objectives and governance frameworks
- Legal, regulatory and contractual considerations
- Information-security strategy, roles and responsibilities
- Enterprise and information-security architecture under the revised outline
- Metrics, reporting and executive communication
Domain 2: Information Security Risk Management
Understand how managers identify, assess, treat, monitor and communicate information-security risk.
- Risk identification, assessment and analysis
- Threats, vulnerabilities, likelihood and business impact
- Risk treatment, acceptance and ownership
- Control selection and monitoring
- Third-party, cloud and emerging risk
- Risk communication and reporting
Domain 3: Information Security Program
Learn how an information-security program is designed, resourced, operated and improved.
- Program development, implementation and management
- Resources, roles and responsibilities
- Policies, standards, procedures and control integration
- Asset, data, identity and access considerations
- Third-party security and awareness
- Program metrics, monitoring and continuous improvement
Domain 4: Incident Management
Develop the management judgement needed to prepare for, respond to and learn from information-security incidents.
- Incident-management planning and readiness
- Roles, escalation and communication
- Detection, classification, response and containment
- Business impact, recovery and continuity
- Investigation and evidence context
- Post-incident review and program improvement
How CISM Management Decisions Are Practised in Class
Third-party security incident
An Australian organisation’s critical SaaS provider reports unauthorised access affecting customer information. Technical teams want immediate containment, operations is concerned about continuity, and executives need a clear risk and communication plan.
Learners work through the management response
- Determine what must be escalated and who owns each decision.
- Prioritise business impact, regulatory context and service continuity.
- Identify the evidence leaders need before taking action.
- Apply incident-governance, communication and stakeholder responsibilities.
- Identify security-program gaps exposed by the event.
- Set remediation priorities, metrics and management follow-up.
Worked management response: First establish incident governance and decision ownership, confirm scope and business impact, and preserve appropriate evidence. Leadership should assess continuity risk and third-party dependencies, determine whether relevant notification or reporting obligations may apply, coordinate internal and external communication, and prioritise containment and recovery according to enterprise risk. Once stabilised, the organisation should complete root-cause and control-gap analysis and track remediation through the security programme.
Why this matters for CISM: several actions may be technically valid. The exam often tests which management action or sequence is most appropriate given governance, risk ownership and business priorities.
Original EduDelphi teaching scenario. Not an official, live or recalled ISACA exam question.
CISM Exam Format, Results, Scheduling & Retake Rules
| Exam detail | Current rule |
|---|---|
| Questions | 150 multiple-choice questions |
| Duration | 4 hours |
| Scoring scale | 200–800 |
| Passing score | 450+ |
| Registration | Continuous |
| Eligibility period | 6 months |
| Earliest appointment | 48 hours after registration payment |
| Appointment visibility | Up to 90 days ahead |
| Rescheduling | Free if changed at least 48 hours before the appointment |
| Delivery | Authorised PSI centre or remote proctoring |
| Preliminary result | Shown after completing the exam |
| Official result | Within 10 working days |
Always check the current official CISM page and candidate guide before booking.
CISM Certification Requirements: Exam vs Experience
Prepare and pass
Complete your preparation and pass the official CISM examination.
Build and verify experience
Meet the current relevant experience requirement across the required CISM domains.
Apply to ISACA
Submit the certification application within five years of passing, including experience verification.
Maintain the credential
Meet continuing professional education, fee and ethics requirements after certification.
ISACA currently requires at least five years of professional information-security management experience across at least three of the four CISM domains. Qualifying experience must fall within the 10 years preceding the certification application, and candidates must apply for certification within five years of passing the examination. Experience is verified as part of the application process. ISACA makes the final determination.
Experience substitutions may be available under current ISACA rules. The allowance depends on qualifying education, certifications and experience and does not remove the need to satisfy ISACA’s overall certification requirements. Confirm the current substitution rules before relying on them in your certification timeline.
Official reference: Get CISM Certified.
CISM Course Fees vs Official ISACA Costs
There are two separate cost paths. Understand them before enrolling so the preparation fee and official certification charges are never confused.
CISM preparation packages from A$750
Live teaching, 40+ guided hours, LMS, recordings, 3,000+ resources, multiple mocks, revision and direct support.
Your written quotation confirms GST treatment, guided hours, delivery mode, LMS and recording access, practice resources, mocks, trainer support and any included third-party study materials before enrolment.
Official exam and certification
Exam registration, later certification application and ongoing maintenance charges are paid directly to ISACA.
EduDelphi does not collect or control these official charges.
| Current ISACA-published item | Member | Non-member |
|---|---|---|
| CISM examination | US$575 | US$760 |
| Certification application | US$50 | US$50 |
| Annual certification maintenance | US$45 | US$85 |
Official pricing can change. Verify fees with ISACA before payment. Static AUD conversions are intentionally not shown because exchange rates move.
Recommended CISM Study Plan for Working Professionals
A good CISM plan builds knowledge first, then progressively increases scenario difficulty, integration and timed practice.
Learn the domains
Use live teaching and the LMS to understand the four domains and their management relationships.
Practise by domain
Work through questions topic by topic and review every reasoning error.
Integrate scenarios
Practise decisions that cross governance, risk, program and incident responsibilities.
Complete timed mocks
Use final mocks, weak-domain revision and exam strategy before the PSI appointment.
How CISM Knowledge Applies in Australian Security Roles
The CISM examination is global. EduDelphi uses selected Australian contexts to help learners connect management principles with the environments they may encounter locally.
Privacy and breach response
Connect incident decisions, governance and communication with Privacy Act and Notifiable Data Breaches context.
APRA-regulated sectors
Use CPS 234 as context for security capability, responsibilities, controls and incidents, and CPS 230 for operational resilience, critical operations and material service-provider risk. The updated CPS 230 took effect on 1 July 2026.
Critical infrastructure
Consider security governance, risk ownership, resilience and third-party dependencies in SOCI Act environments.
Government environments
Connect governance and program thinking with ASD’s September 2026 ISM and Essential Eight / evolving Essentials guidance.
Technology and SaaS
Examine cloud, supplier, identity, data and incident decisions in fast-changing organisations.
Executive reporting
Translate security risk and program performance into priorities, metrics and decisions for senior leadership.
CISM Career Paths in Australia
CISM knowledge is relevant to management and advisory roles where professionals must align security with enterprise objectives and risk.
- Information Security Manager
- Cybersecurity Manager
- GRC or Technology Risk Manager
- Security Program Manager
- Security Consultant
- Incident or Resilience Manager
- CISO-track leadership roles
CISM vs CISA vs CISSP vs CRISC
| Credential | Typical career alignment | Primary emphasis |
|---|---|---|
| CISM | Security managers and program leaders | Governance, risk, security programs and incidents |
| CISA | IT audit and assurance professionals | Auditing information systems and controls |
| CISSP | Experienced cybersecurity professionals | Broad technical and managerial security knowledge |
| CRISC | Technology-risk and control professionals | Enterprise IT risk and controls |
No credential is universally better. Choose according to the work and responsibility you want. Explore EduDelphi’s CRISC course in Australia if technology-risk management is your primary goal.
Security Leadership Salary References in Australia
Robert Half’s 2026 Australian Salary Guide provides role benchmarks for security leadership. These are projected gross starting salaries excluding bonuses, benefits and super—not earnings attributable to CISM certification.
| Role | 25th percentile | Mid | 75th percentile |
|---|---|---|---|
| Cyber-Security Manager | A$160,000 | A$180,000 | A$205,000 |
| Chief Information Security Officer | A$220,000 | A$265,000 | A$305,000 |
Source: Robert Half Australia Salary Guide. Treat these as market context only; actual pay varies by seniority, location, industry and responsibility.
Meet Your CISM Trainer
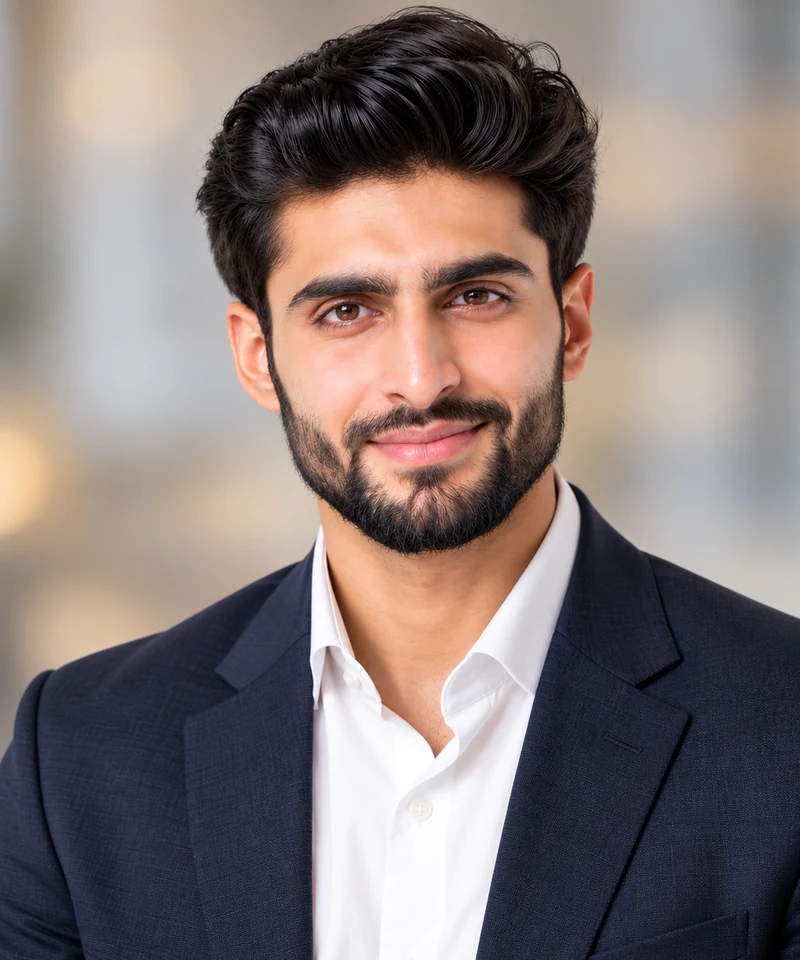
Kashif Akhtar
Qualified Engineer, CSCP, PMP, CISA, CISM, CRISC, CDPSE
Kashif brings 30+ years of practical experience across technology, cybersecurity, IT governance and enterprise risk, including work within multinational and complex operating environments.
For Australian CISM learners, he connects security governance, risk management, security-program development and incident management with practical situations from banking, mining, utilities, technology and other large organisations. His teaching is strongly exam-focused, helping candidates master ISACA question logic, management-level judgement, prioritisation and scenario interpretation rather than relying on technical memorisation alone.
What EduDelphi Learners Say
Institution-wide learner feedback on teaching quality, practical explanation and support across EduDelphi professional training.
“Good diverse classmates, some experienced and some learning. I liked the combination of practical notes and explanation of why something is important, not just how to do it.”
“Great experience in learning with Delphi, very professional staff, detailed training, and a strong overall learning environment.”
“Simple and logical explanations helped me understand the concepts and apply them in exam questions. The trainers have excellent practical knowledge.”
Corporate CISM Training for Australian Security & Risk Teams
Build a shared management language across security, technology risk, governance and assurance teams through private CISM preparation.
- Live online, classroom, hybrid and onsite delivery
- Scheduling around operational commitments
- Contextualised governance, risk and incident scenarios
- LMS, practice resources and multiple mocks
- Private cohorts and direct trainer support
Live Online, Classroom, Private & Corporate CISM Training
Live online CISM preparation is available nationwide, including Sydney, Melbourne, Brisbane, Perth, Adelaide, Canberra and regional Australia. Classroom, private and onsite delivery can be arranged subject to cohort, location and scheduling requirements.
Live online
Instructor-led classes with interaction, recordings and direct support.
Classroom
Face-to-face delivery can be arranged based on cohort and location requirements.
Private
One-to-one and tailored preparation around an individual target date.
Corporate
Private team delivery online, onsite or in a hybrid format.
Maintaining the CISM Certification
CISM is maintained through continuing professional education, annual reporting and compliance with ISACA requirements.
20 CPE annually
Report at least 20 continuing professional education hours each year.
120 CPE over three years
Meet the minimum across the three-year reporting cycle.
Fees and ethics
Pay the annual maintenance fee and comply with ISACA’s professional ethics requirements.
Verify current rules through ISACA’s CISM maintenance guidance.
CISM Course & Certification FAQs
1. What is CISM certification?
CISM is ISACA’s Certified Information Security Manager credential. It focuses on security governance, risk management, security-program leadership and incident management.
2. Is CISM suitable for complete beginners?
You can begin learning and take the exam before meeting the full experience requirement, but CISM is management-oriented. Candidates benefit from exposure to security, risk, audit, governance or technology operations.
3. Can I take the exam without five years of experience?
Yes. Examination eligibility and certification eligibility are separate. You can pass the exam first, but you must later meet ISACA’s experience and application requirements to receive the credential.
4. Which syllabus applies in November 2026?
Exams taken up to 2 November use the earlier outline. Exams from 3 November 2026 use the revised outline. EduDelphi is ready to support both routes according to the learner’s booked examination date.
5. How many questions are in the CISM exam?
The official CISM examination contains 150 multiple-choice questions and allows four hours.
6. What is the CISM passing score?
ISACA reports scores on a 200–800 scale. A scaled score of 450 or higher is required to pass. It is not a raw percentage or a simple 450 ÷ 800 calculation.
7. Can I take the CISM exam online from Australia?
Yes. ISACA currently offers the CISM examination through authorised PSI test centres and remote proctoring. Remote appointments remain subject to PSI availability, identity requirements, system compatibility and testing-environment rules. Check your computer and environment before booking.
8. How much does the official CISM exam cost?
Current ISACA-published pricing is US$575 for members and US$760 for non-members. Verify pricing with ISACA before payment.
9. Is the ISACA exam fee included in EduDelphi tuition?
No. EduDelphi tuition and official ISACA charges are separate unless a specific written offer says otherwise.
10. How long should I study for CISM?
The right duration depends on experience, weekly study capacity and examination date. EduDelphi uses 40+ guided hours plus structured practice, mocks and revision; private and flexible routes can adapt the preparation sequence.
11. Is CISM better than CISA or CISSP?
No credential is universally better. CISM is strongest for security management and governance; CISA focuses on IT audit; CISSP covers a broad security body of knowledge.
12. Does CISM expire?
The credential must be maintained through annual and three-year CPE requirements, fees and compliance with ISACA policies.
13. Does EduDelphi issue the CISM certification?
No. ISACA awards CISM. EduDelphi provides independent training, practice, mocks and candidate support.
14. What happens if I do not pass the CISM exam?
ISACA currently permits up to four attempts in a rolling 12-month period. After the first unsuccessful attempt, you must wait 30 days before attempt two; subsequent permitted retakes require 90-day waiting periods. A new exam fee applies to each attempt.
15. Can EduDelphi train a corporate team in Australia?
Yes. Private live online, classroom, hybrid and onsite routes are available for Australian organisations.
Get CISM Course Fees & the Next Australian Batch
Request the current syllabus, AUD tuition guidance and the delivery route that fits your target examination date.
- Current or revised-outline preparation
- Live online, classroom, private and corporate options
- Evening and weekend availability
- 40+ guided hours and 3,000+ resources
Speak with EduDelphi Australia
Phone: +61 4 8598 4141
Email: [email protected]
Australia office: MacArthur Ave, Hamilton QLD 4007
EduDelphi tuition is enquiry-led. Official ISACA charges are paid separately.