CISSP Course in Oman for Experienced Security Professionals
Prepare for the Certified Information Systems Security Professional® (CISSP®) exam through 40+ guided live hours, structured teaching across all eight domains, 3,000+ CISSP practice questions, multiple CAT-style simulations, recordings and an advanced learning system.
EduDelphi provides independent CISSP preparation and candidate support. ISC2 controls the official examination, experience review, endorsement, certification and maintenance requirements.
CISSP Course Snapshot
- 40+ guided live training hours
- Muscat classroom, live online, hybrid, private, self-paced and corporate routes
- Flexible weekday, evening, weekend and fast-track batches
- 3,000+ CISSP practice questions and extensive revision resources
- Multiple timed CISSP exam simulations with no-backtracking practice, mixed-domain questions, pacing review and CAT-format strategy
- Recordings, notes, mind maps, flashcards and structured study plans
- Individual doubt support, mock analysis and weak-area review
- Exam, experience, endorsement, career and job-search support
Choose a CISSP Learning Route That Fits Your Role
Course tuition is enquiry-led because the selected live, classroom, hybrid, private, self-paced or corporate route changes the package. Official ISC2 exam and maintenance charges remain separate.
EduDelphi CISSP Course Fee
- Request the current Oman training fee
- Compare weekday, evening, weekend and fast-track batches
- Review active instalment and early-bird options
- Receive the complete written inclusion list
- Discuss voucher or retake-support options for the selected package
| Official ISC2 cost or requirement | Current Oman/Middle East reference |
|---|---|
| CISSP exam | US$749 |
| Exam rescheduling | US$50 |
| Exam cancellation | US$100 |
| Retake | New exam registration or applicable official product |
| CISSP annual maintenance fee | US$135/year |
| Associate of ISC2 annual maintenance fee | US$50/year |
| Full CISSP CPE requirement | 120 CPE credits over three years |
| Associate CPE requirement | 15 CPE credits/year |
Official-fee reference checked in September 2026 against ISC2 exam pricing. Taxes, location and current terms can change the final amount. Always verify the live ISC2 checkout before paying.
Join from Muscat or Learn Live Online Anywhere in Oman
Prepare without reducing course depth around a demanding security, IT, risk or governance role. Choose Muscat classroom sessions, live online classes, hybrid learning, one-to-one preparation, a complete self-paced route or an employer cohort.
- Weekday, evening, weekend and fast-track choices
- Complete recordings and structured LMS reinforcement
- Private and one-to-one teaching where required
- Repeat-session and later revision-batch support
- Live online access from Muscat, Sohar, Salalah, Nizwa, Sur, Duqm and elsewhere
- Private onsite and virtual corporate programmes
What Is CISSP Certification?
CISSP is a senior cybersecurity credential that validates broad technical and managerial knowledge across governance, risk, architecture, networks, identity, assessment, operations and software security.
EduDelphi CISSP Course
Independent live training, extensive practice questions, CAT-style simulations, learning resources, faculty support and certification-path guidance.
ISC2 CISSP Exam
A three-hour Computerized Adaptive Test containing 100–150 items across the eight current domains.
CISSP Certification
Awarded by ISC2 after the examination, qualifying experience, certification application, endorsement, ethics and maintenance requirements are satisfied.
A candidate who passes without the required experience can apply for Associate of ISC2 status. Associates are not CISSP-certified and should not use the CISSP designation until the certification requirements are completed.
What Is Included in the EduDelphi CISSP Course?
The course follows a deliberate learning loop: diagnose knowledge, understand each domain, apply security judgement, practise questions, analyse errors, complete CAT-style simulations and retest weak areas.
40+ Guided Hours
Faculty-led teaching across every current CISSP domain, supported by practical enterprise cases.
3,000+ Questions
Topic drills, domain sets, mixed scenarios, timed practice and detailed answer review.
Timed CAT-Format Practice
Mixed-domain simulations, no-backtracking discipline, three-hour pacing and readiness review.
Advanced LMS
Recordings, learning resources, practice history, progress visibility and organised revision support.
Revision Resources
Notes, domain maps, flashcards, quick-reference sheets, study plans and visual summaries.
Individual Support
One-to-one doubt clarification, mock debriefs, error diagnosis and targeted weak-area review.
Repeat and Reinforce
Repeat relevant sessions and join later revision batches where appropriate.
End-to-End Guidance
Support with exam planning, official costs, experience mapping, Associate status, endorsement and professional positioning.
EduDelphi CISSP LMS and Exam-Readiness System
The platform helps working professionals convert learning activity into measurable domain readiness rather than simply storing recorded lectures.
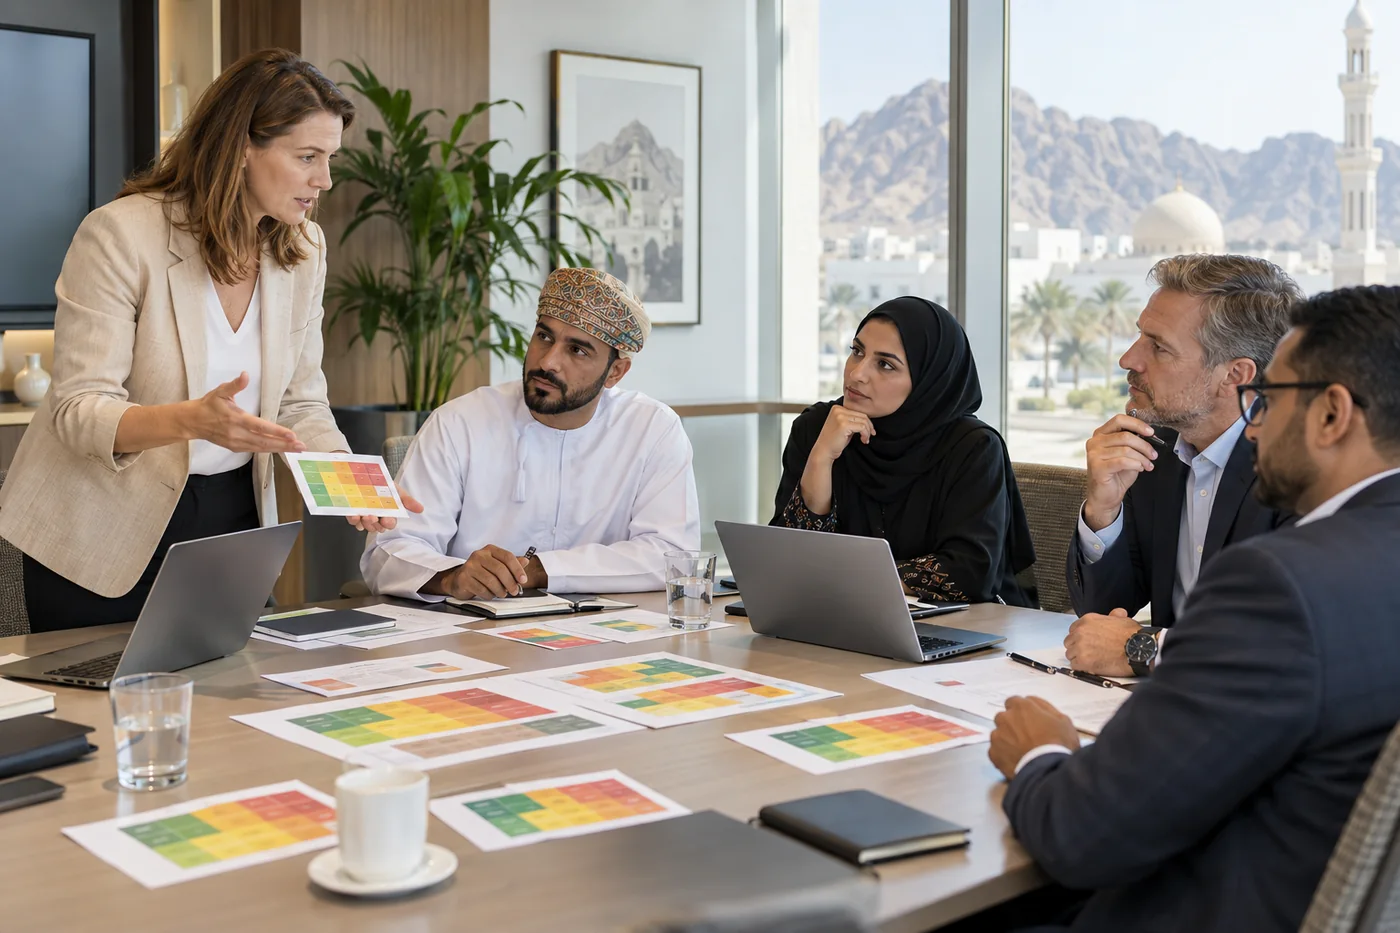
From Domain Diagnostics to Full CISSP Exam Simulation
CISSP questions frequently contain several technically plausible choices. Learners practise identifying the response that best reflects risk, ownership, sequencing, business impact and senior security judgement.
Initial Diagnostic
Identify where professional experience transfers—and where the exam requires broader domain knowledge.
Domain Drills
Build core concepts through focused sets before integrating them into cross-domain cases.
Mixed Scenarios
Recognise the domain, business objective, accountable owner and decision the question is testing.
Timed Tests
Build interpretation speed and concentration without sacrificing judgement.
CAT-Format Practice
Practise the behaviours that matter in CISSP CAT—committing to each answer, managing three-hour pacing, handling mixed-domain questions and maintaining judgement under uncertainty.
Answer Debriefs
Understand why the most appropriate response is stronger than close alternatives.
Error Diagnosis
Classify errors by knowledge, scope, ownership, sequencing, evidence or technical bias.
Targeted Retesting
Revisit weaker domains and compare performance before sitting the examination.
The system combines 3,000+ CISSP practice questions with diagnostics, explanations, mixed cases, timed tests, multiple CAT-style simulations, faculty debriefs, individual weak-area review and targeted retesting.
Eight CISSP Domains and Current Exam Weightings
The current official outline took effect on 15 April 2024. If a provider or question source shows different weights, verify that it matches the active ISC2 outline before relying on it.
1. Security and Risk Management — 16%
Ethics, governance, security concepts, legal and regulatory context, policy, business continuity, personnel security, risk management, threat modelling, supply-chain risk and awareness.
Teaching emphasis: connect security decisions with organisational objectives, ownership, risk appetite and due care.
2. Asset Security — 10%
Information and asset classification, secure handling, ownership, lifecycle, retention, destruction, data states and protection methods.
3. Security Architecture and Engineering — 13%
Secure design principles, security models, cryptography, system vulnerabilities, cloud and distributed environments, physical security, resilience and lifecycle decisions.
4. Communication and Network Security — 13%
Secure network architecture, protocols, segmentation, communications, remote access, wireless, third-party connectivity and monitoring.
5. Identity and Access Management — 13%
Identification, authentication, federation, access-control models, authorisation, privileged access and identity lifecycle management.
6. Security Assessment and Testing — 12%
Assessment strategies, control testing, vulnerability assessment, penetration testing, audit evidence, reporting and remediation.
7. Security Operations — 13%
Investigations, logging, monitoring, configuration, change, incident response, recovery, resilience, continuity and disaster recovery.
8. Software Development Security — 10%
Security in the software lifecycle, development ecosystems, application controls, testing, acquired software, APIs and secure coding.
Source: current ISC2 CISSP Exam Outline. EduDelphi’s preparation methodology and mocks are independent course resources, not additional official CISSP domains.
See How CISSP Connects Security Decisions
An Oman-based critical-infrastructure operator plans to move a customer-facing platform to a cloud environment. A review identifies weak privileged-access recertification, unclear log ownership and a recovery objective that does not match the business dependency. Launch remains commercially important.
What should the security professional do FIRST?
- Implement an immediate compensating control and proceed while the long-term remediation is planned.
- Conduct a formal risk assessment, clarify business impact and escalate treatment options to the accountable risk owner.
- Delay the migration until every architecture component meets the organisation’s security baseline.
- Transfer responsibility contractually to the cloud provider and document the residual risk.
Before selecting, transferring or enforcing a treatment, the professional should establish the exposure, business impact, accountable owner and decision authority. A compensating control may be part of the final response, but it should follow the risk decision rather than replace it.
Original EduDelphi scenario for teaching. It is not official, recalled or live ISC2 examination content.
Exam Eligibility, Experience and Full CISSP Certification
Anyone may prepare for and sit the CISSP examination, but full certification normally requires five years of cumulative qualifying professional experience across at least two of the eight CISSP domains. Full-time, qualifying part-time work and documented internships may count under current ISC2 rules.
| Experience type | Current ISC2 treatment | Practical meaning |
|---|---|---|
| Full time | At least 35 hours/week for four weeks | Accrues as one month of qualifying experience. |
| Part time | 20–34 hours/week | 1,040 hours equals six months; 2,080 hours equals 12 months. |
| Internship | Paid or unpaid may qualify | Acceptable documentation on organisational or registrar letterhead is required. |
| One-year waiver | Qualifying degree or one currently approved credential | Only one year can be waived; the degree and credential routes cannot be stacked. |
Do not assume an older certification still qualifies. ISC2 revised the list and its inclusion criteria. A qualifying degree or one credential on the current ISC2 waiver list can reduce the requirement by a maximum of one year; the two routes cannot be combined to remove two years.
Passed CISSP Without Five Years? Use the Associate of ISC2 Route
Candidates may sit the CISSP exam before completing the experience requirement. After passing, the correct interim status is Associate of ISC2—not “Associate CISSP.”
| Associate item | Current position |
|---|---|
| Exam | You may sit CISSP before having five years of experience. |
| Status after passing | Apply as Associate of ISC2, not as a CISSP. |
| Experience window | Up to six years for the CISSP route. |
| Associate maintenance | US$50 AMF and 15 CPE credits annually. |
| After completing experience | Submit the certification application and endorsement before the Associate period expires. |
| Upgrade | The current US$85 AMF difference applies when the year’s Associate AMF has already been paid. |
| Title rule | Do not describe yourself as CISSP until ISC2 awards full certification. |
Source: current Associate of ISC2 guidance and member-maintenance rules.
How the Current CISSP CAT Exam Works
The adaptive format selects later items partly from earlier responses. Candidates must read carefully and commit to the best available answer because completed items cannot be revisited. The rules below reflect current ISC2 CAT guidance.
| Official current item | What candidates should plan for |
|---|---|
| Delivery | Computerized Adaptive Testing at authorised Pearson testing centres. |
| Items | 100–150 multiple-choice and advanced item types, including unscored pretest items that cannot be identified. |
| Duration | Three hours maximum; breaks are included within the examination time. |
| Review | No backtracking after an answer is finalised. |
| Passing standard | 700 out of 1,000 scaled points—not a simple 70% raw score. |
| Exam purchase window | Schedule and sit the exam within 365 days of purchase under current terms. |
| Result | Pass/fail result after completion; eligible unsuccessful candidates receive domain-level diagnostic feedback. |
| Retakes | 30 test-free days after attempt one, 60 after attempt two and 90 after attempt three or later. |
| Attempt limit | Maximum four attempts for the certification in a 12-month period. |
No Backtracking
Practise reading the complete scenario before finalising the response.
Breaks Use Time
Build endurance and plan breaks inside the three-hour clock.
Every Attempt Costs Again
Each retake requires a new official exam registration fee.
Why Your CISSP Exam May End at 100, 120 or 150 Questions
CISSP CAT does not give every candidate the same number of items. After the 100-item minimum, the algorithm may continue until it has enough statistical evidence or the 150-item maximum is reached.
| What happens | What it means |
|---|---|
| Exam ends after 100 items | CAT reached sufficient statistical confidence in the pass/fail decision. |
| Exam continues after 100 | CAT needs more evidence; continuing does not by itself mean pass or fail. |
| Exam reaches 150 | The maximum-length rule applies and the final ability estimate determines the result. |
| 25 pretest items at minimum length | They are unscored and cannot be identified, so treat every item as scored. |
| No backtracking | Every submitted answer is final. |
| The exam feels difficult | This is not evidence of failure; CAT adapts item difficulty to the candidate. |
ISC2 states that candidates who do not answer at least 75 scored operational items plus 25 pretest items within the three-hour limit automatically fail. Build pacing discipline without rushing the judgement each scenario requires.
Complete the ISC2 Endorsement and Certification Process
Passing is followed by a separate certification application. Candidates should document experience and plan endorsement promptly rather than treating the result as the final step.
ISC2 currently allows candidates to request endorsement assistance. Proof of employment is required, and ISC2—not EduDelphi—decides whether the experience and application meet its requirements.
Best Aligned to Experienced Security, Technology and Risk Professionals
CISSP is broad and senior-level. It is strongest for professionals who need to connect technical security, architecture, operations, governance and enterprise risk.
Security Professionals
Security engineers, architects, consultants and operations leaders expanding into broader responsibility.
Technology Leaders
IT managers, infrastructure and cloud professionals responsible for enterprise security decisions.
GRC and Risk
Professionals connecting security requirements with governance, assurance, risk and compliance.
Leadership Path
Experienced practitioners progressing toward security management, architecture or programme leadership.
Security+ or SSCP may offer a more appropriate foundation. CISA is more audit-led, CISM is management-led, CRISC centres on IT risk and controls, and CCSP is cloud-security specific.
Cybersecurity Capability Matters Across Oman’s Digital Economy
Oman’s National Information Safety Centre links cybersecurity capability with Vision 2040 and the growth of the digital economy. The national cybersecurity indicator programme assesses government organisations across legal, technical, organisational, capacity-building and cooperation pillars.
Oman reported 97.02 in the 2024 Global Cybersecurity Index and placement in the top readiness tier. The 2026 Information Technology Crimes Law and Cloud-First policy further strengthen the local relevance of security governance, architecture, cloud controls, data protection, IAM, resilience and incident response.
CISSP knowledge can support professionals working across banking, oil and gas, utilities, telecom, healthcare, government-linked organisations, logistics and critical infrastructure. Employer requirements still depend on the role; the credential does not guarantee employment.
Oman examples are used to teach application. The CISSP examination follows the global ISC2 outline and is not an Oman-law examination.
Local Application Themes
- Cloud transformation and shared responsibility
- Critical-infrastructure security and resilience
- Third-party and supply-chain security risk
- Privileged access and identity governance
- Incident readiness and recovery priorities
- Data classification and lifecycle protection
- Security metrics and executive communication
- Secure software and technology acquisition
Build a Stronger Enterprise-Security Profile
Course support extends beyond exam study while avoiding employment guarantees. The team helps learners communicate their existing experience and newly strengthened security breadth more effectively.
CV Positioning
Clarify security, architecture, risk, operations and leadership responsibilities.
LinkedIn Optimisation
Improve professional positioning for relevant cyber and technology roles.
Application Support
Plan targeted applications rather than relying on high-volume generic submissions.
Recruiter Outreach
Build concise, role-relevant messages and a practical follow-up approach.
CISSP vs CISM vs CISA vs CRISC vs CCSP vs Security+
The strongest credential is the one aligned with the responsibility you want to take on next.
| Qualification | Core focus | Best aligned when |
|---|---|---|
| CISSP | Broad security architecture, engineering, operations, governance and risk | You need senior cybersecurity breadth across the enterprise. |
| CISM | Information-security governance, programme, risk and incident management | You are progressing toward security-management responsibility. |
| CISA | IT audit, assurance, controls and governance | Audit and assurance are central to the role. |
| CRISC | IT risk identification, assessment and control | Technology risk and control design are central. |
| CCSP | Cloud security architecture, governance and operations | Cloud-security responsibility is the specialist focus. |
| Security+ | Foundational security concepts and operational knowledge | You need an earlier-career cybersecurity foundation. |
Also compare the ISO/IEC 27001 Lead Auditor course in Oman and ISO/IEC 27001 Lead Implementer course in Oman when your focus is implementing or auditing an information security management system.
Learn the CISSP Mindset with Practical Security Leadership Context
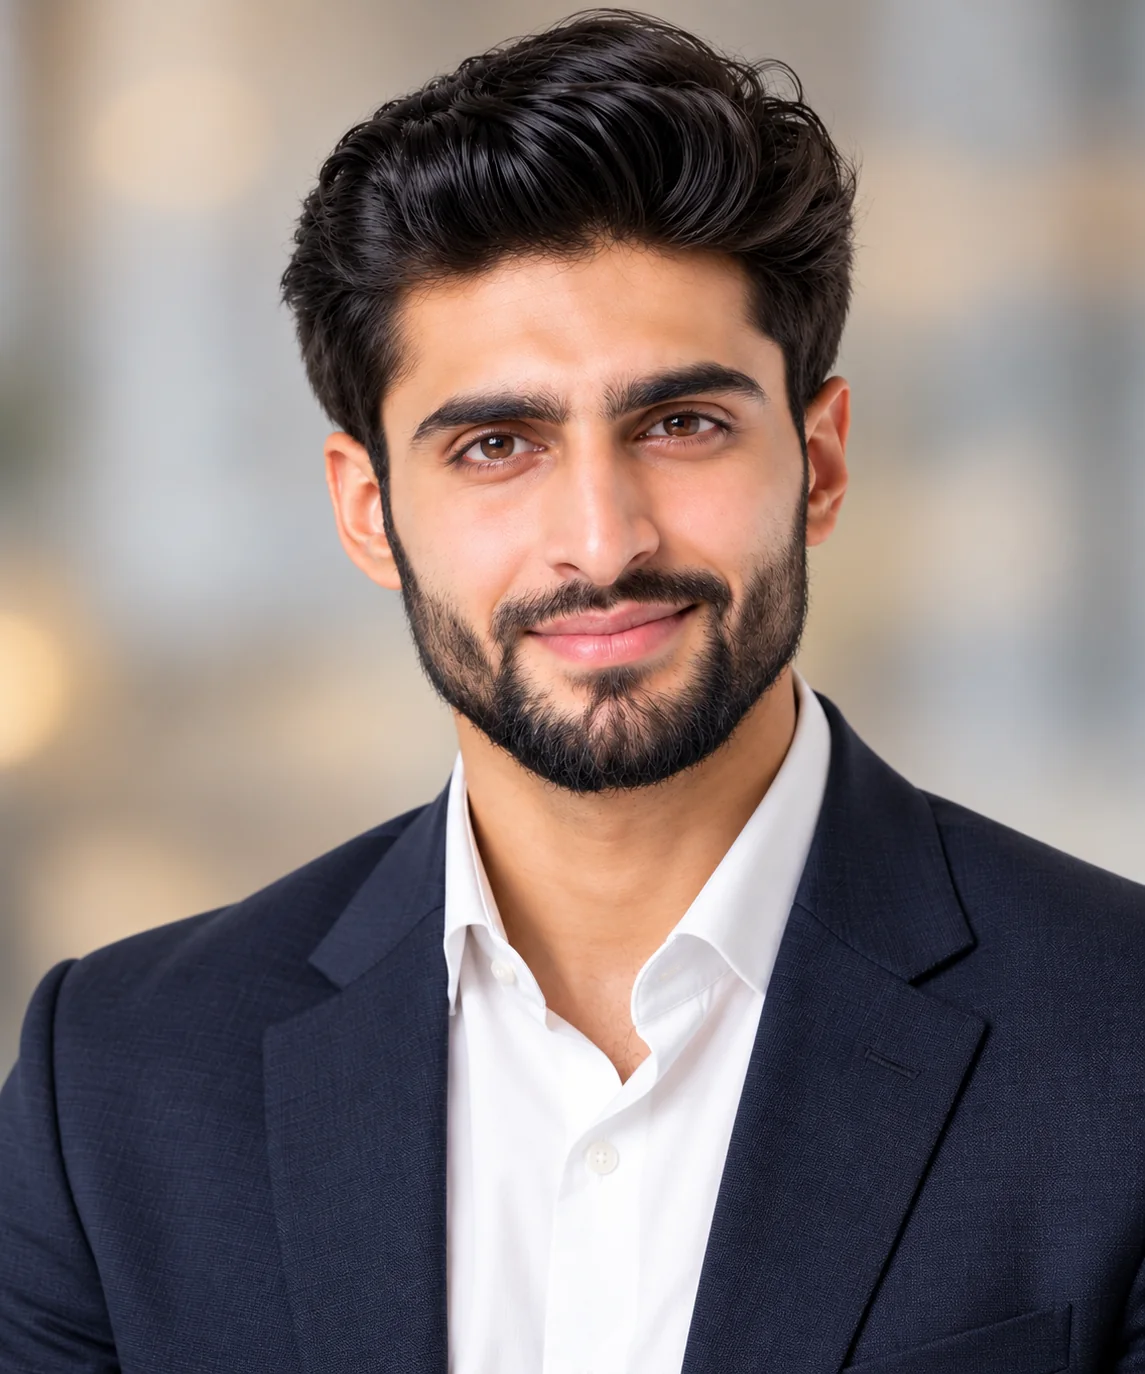
Kashif Akhtar
CISSP Faculty | CISA | CISM | CRISC | CDPSE | PMP | CSCP | Qualified Engineer
30+ Years in Cybersecurity, Technology Risk & Enterprise Systems | 13+ Years in Professional Certification Training
Kashif brings more than 30 years of practical experience across cybersecurity, enterprise technology, IT risk, governance and large-scale systems, including senior exposure within multinational and complex operating environments.
For CISSP learners in Oman, he connects the eight ISC2 domains with security challenges faced across oil and gas, banking, utilities, telecom, government-linked entities and critical infrastructure. His sessions cover security and risk management, architecture, networks, IAM, security assessment, operations, incident response and software security through realistic enterprise scenarios.
Kashif is particularly strong at teaching the CISSP mindset—how to think as a senior security professional rather than simply select the most technical answer. Candidates learn to approach risk-based decisions, prioritisation, governance, architecture trade-offs and “best, first or most appropriate” questions.
His classes combine concept clarity, real security cases, intensive question practice, mock analysis and targeted revision, building both exam readiness and stronger enterprise-security judgement.
Use CISSP Recordings and Resources Around a Demanding Schedule
Self-paced CISSP is available as a standalone route and as reinforcement within the live training ecosystem. Learners can revisit domain explanations, repeat practice, use revision resources and prepare around travel or shifting work commitments.
- Complete domain learning route
- Recorded lectures and structured resources
- Practice questions and mock preparation
- Live and individual support options where selected
- Repeat and revision access within the applicable package
Not Sure Which Format Fits?
Share your current role, weekly availability, target examination timing and preferred support level. The team will recommend an appropriate live, classroom, hybrid, private, self-paced or corporate route.
Build Shared Security Knowledge Across Technology and Risk Teams
Private CISSP cohorts are available for cybersecurity, IT, architecture, engineering, cloud, audit, GRC and technology-risk teams. Delivery can be virtual, classroom-based or onsite across Oman.
- Pre-course diagnostics and role mapping
- Customised domain emphasis and practical cases
- Private schedules for working teams
- Attendance and progress visibility
- Question checkpoints and mock planning
- Manager-facing summaries and readiness reporting
- Capability workshops without mandatory exam registration
Muscat Office and Oman-Wide CISSP Support
EduDelphi Oman – Muscat
Street 3701, Al Ghubrah South
Postal Code 130, Muscat, Oman
Support Across Oman
Use the Muscat office for local course guidance while joining through classroom, live online, hybrid, private or corporate delivery from anywhere in the Sultanate.
Common Questions from CISSP Candidates in Oman
What does CISSP stand for?
Is CISSP recognised in Oman?
Can I take the CISSP exam without five years of experience?
What is Associate of ISC2?
What work experience is required for CISSP?
Can a degree or another credential reduce the experience requirement?
How many questions are on the CISSP exam?
Can I take the CISSP exam online from home in Oman?
Can I change an earlier answer in the CISSP CAT exam?
What score is required to pass CISSP?
What happens if I do not pass CISSP?
What happens after I pass the CISSP exam?
Who can endorse my CISSP application?
How do I maintain CISSP?
How long does CISSP preparation take?
Is CISSP the same as ISO/IEC 27001 training?
Is the CISSP exam available in Arabic?
Are exam-voucher or retake-support options available?
Get Fees, Syllabus and Current CISSP Batch Options
Share your current role, experience, preferred delivery mode and target examination timing. The Oman team will send the current fee structure, active schedules, complete inclusions and an appropriate preparation recommendation.
- Training and official-cost breakdown
- Weekday, evening, weekend and fast-track options
- Experience and Associate-path guidance
- Live, classroom, self-paced, private and corporate routes
Request CISSP Course Details
Get the current Oman course information and speak with the team.
CISSP and Certified Information Systems Security Professional are registered marks of ISC2. EduDelphi provides independent CISSP exam preparation and does not award the credential.