CRISC Course Fees, Next Batch & What Is Included
Prepare through a complete learning route built for Australian technology-risk, cybersecurity, GRC, audit and controls professionals. Multiple live batches run through the year, with online, classroom, private and team options.
From A$750
Choose the preparation package and delivery route that fit your target exam date and level of support.
38+ guided hours
Build the four CRISC domains through live explanation, risk scenarios, question debriefs and revision.
3,000+ resources
Use questions, practice resources, timed mocks, study guides, revision assets and recordings.
Flexible schedules
Daytime, evening and weekend options support professionals across Australian time zones.
Why Choose EduDelphi for CRISC Training in Australia?
CRISC questions test risk-based judgement. Our learning system connects expert teaching, practice, revision and direct support so candidates can reason through enterprise risk decisions—not memorise disconnected definitions.
Learn with an experienced CRISC practitioner
Kashif Akhtar brings 30+ years across IT risk, cybersecurity, technology governance and enterprise systems, plus 13+ years in professional certification training.
38+ guided live hours
Build every domain systematically through live classes, practical risk context and exam-focused review.
AI-supported LMS
Keep recordings, domain resources, practice questions, revision documents and mocks organised in one learning environment.
3,000+ practice resources
Progress from domain questions to integrated scenarios, answer analysis and timed final practice.
Multiple mock exams
Practise pace, stamina and prioritisation while identifying weaker domains before the official exam.
Human support throughout
Use doubt solving, study planning, trainer feedback and flexible catch-up options around demanding work schedules.
What Is CRISC Certification and Who Issues It?
CRISC stands for Certified in Risk and Information Systems Control. It is designed for professionals who identify and assess enterprise IT risk, plan risk responses, report risk and help design, monitor and improve information-systems controls.
ISACA
Sets the CRISC exam, evaluates certification applications and governs ongoing maintenance requirements.
CRISC
The professional credential awarded to candidates who satisfy the examination, experience, application and ethics requirements.
EduDelphi
Provides independent CRISC training, question practice, mocks, LMS resources and candidate support. EduDelphi does not award CRISC.
Explore related risk-management courses in Australia and cybersecurity courses in Australia.
Who Should Take CRISC Training in Australia?
Technology-risk professionals
For people who identify, assess, treat, monitor or report technology and cyber risk.
Cybersecurity and GRC teams
For professionals connecting security controls with enterprise objectives, risk appetite and accountability.
IT auditors and assurance teams
For audit professionals extending their capability into risk ownership, response and control design.
Control and compliance professionals
For practitioners who design, test, monitor or improve technology-related controls.
IT and security managers
For leaders responsible for third parties, resilience, governance, risk reporting or control performance.
Consultants and career movers
For advisers and experienced professionals building a stronger route into IT risk and GRC work.
What Is Included in EduDelphi CRISC Training?
Teaching, practice, revision and candidate support are designed as one connected preparation experience.
| Learning component | How it supports CRISC preparation |
|---|---|
| 38+ hours of live training | Build each domain with direct explanation, business context and scenario reasoning. |
| AI-supported LMS and recordings | Keep classes, learning resources and revision organised around work and travel. |
| 3,000+ practice resources and questions | Strengthen risk judgement, prioritisation and cross-domain decision making. |
| Multiple timed mock exams | Practise full-exam pacing and identify domains requiring final review. |
| Study guides and books | Follow a structured route through the current CRISC syllabus. |
| Revision documents and quick-reference assets | Consolidate frameworks, risk concepts, KRIs, controls and exam logic. |
| Doubt solving and trainer support | Understand why an option is strongest and why plausible alternatives are weaker. |
| Exam and application guidance | Understand official registration, PSI scheduling and later certification steps. |
| Flexible delivery | Choose live online, classroom, private, one-to-one, hybrid, onsite or corporate delivery. |
Current CRISC Exam Content Outline: Effective 3 November 2025
The current CRISC exam outline applies throughout 2026 unless ISACA announces a later revision. Candidates using older books or question banks should make sure their resources reflect the current domain weights and content.
Domain 1: Governance 26%
Understand how organisational strategy, governance, risk capacity and accountability shape technology-risk decisions.
- Enterprise strategy, objectives and governance
- Organisational structure, culture and roles
- Risk appetite, tolerance and capacity
- Legal, regulatory and contractual considerations
- Risk-management frameworks, policies and standards
- Business resilience, ethics and risk culture
Domain 2: Risk Assessment 22%
Learn to identify, analyse and evaluate technology-related risk using credible evidence and consistent methods.
- Risk events, threats, vulnerabilities and asset context
- Risk scenarios, likelihood and business impact
- Current and emerging technology risk
- Data collection, analysis and risk assessment methods
- Risk ownership and stakeholder validation
- Risk registers, inherent risk and residual risk
Domain 3: Risk Response and Reporting 32%
Decide how risk should be treated, monitored, escalated and communicated to decision makers.
- Risk treatment, acceptance, avoidance, transfer and mitigation
- Risk action plans, ownership and accountability
- Key risk indicators and performance measures
- Third-party and supply-chain risk response
- Exception, issue and remediation management
- Risk reporting, communication and escalation
Domain 4: Technology and Security 20%
Connect technology and security controls with the risks they are intended to address.
- Enterprise architecture, infrastructure and applications
- Identity, access, data and cloud considerations
- Systems development and change
- Control design, implementation and monitoring
- Security, privacy, incident and resilience controls
- Control testing, evidence and continuous improvement
Official reference: ISACA CRISC Exam Content Outline.
CRISC Training Built Around Real Risk and Control Artefacts
Candidates learn how concepts appear in actual risk, governance and assurance work—not only as exam definitions.
- Risk registers and risk statements
- Risk appetite and tolerance examples
- Control objectives, control matrices and evidence
- KRIs, thresholds and management dashboards
- Third-party assessments and remediation plans
- Exception, issue and risk-acceptance decisions
- Board, risk-committee and executive reporting
The goal is to connect the CRISC syllabus with the judgement required to identify a material risk, evaluate the strength of a response and communicate what decision is needed.
AI & Emerging Technology Risk
Apply CRISC thinking to AI use cases by identifying business objectives, data and model dependencies, third-party exposure, privacy and security concerns, control ownership, residual risk, approval thresholds and ongoing monitoring.
How CRISC Risk Decisions Are Practised in Class
Third-party technology concentration risk
An Australian organisation depends on one SaaS provider for a critical customer process. The provider has repeated outages, weak subcontractor visibility and limited recovery evidence. Operations wants continuity; procurement wants to renew; the risk committee needs a clear recommendation.
Learners work through the risk response
- Write a clear risk statement with cause, event and business impact.
- Identify the accountable risk owner and relevant stakeholders.
- Assess current controls, evidence quality and residual risk.
- Compare mitigation, transfer, avoidance and acceptance options.
- Define KRIs, thresholds, escalation triggers and reporting.
- Build a practical action plan with ownership and follow-up.
Worked CRISC reasoning: establish decision ownership, validate the risk scenario with operational and supplier evidence, assess the exposure against appetite and identify viable response options. The recommendation should connect control improvements, recovery evidence, contractual rights, concentration exposure and monitoring thresholds to the business decision—not merely list technical weaknesses.
Why this matters: several actions may be useful. CRISC questions often test which action best addresses the risk, who should decide and what evidence is needed first.
Original EduDelphi teaching scenario. Not an official, live or recalled ISACA exam question.
CRISC Exam Format, Results, Scheduling & Retake Rules
| Exam detail | Current rule |
|---|---|
| Questions | 150 multiple-choice questions |
| Duration | 4 hours |
| Scoring scale | 200-800 |
| Passing score | 450 or higher |
| Registration | Continuous |
| Eligibility period | 6 months after registration |
| Eligibility extension | One additional six-month extension is currently available for US$75, subject to ISACA’s timing and cancellation rules. |
| Earliest appointment | 48 hours after registration payment |
| Appointment visibility | Up to 90 days ahead |
| Rescheduling | No charge when changed at least 48 hours before the appointment |
| Delivery | Authorised PSI centre or remote proctoring |
| Preliminary passing status | Shown on screen immediately after completing the exam |
| Official result | Within 10 working days |
Always verify the current official CRISC page and candidate guide before booking.
CRISC Certification Requirements: Exam vs Experience
Prepare
Build the four domains and exam judgement through training and practice.
Pass the exam
Complete the official CRISC examination through ISACA’s testing route.
Verify experience
Document the experience required across the applicable CRISC domains.
Apply and maintain
Submit the application, then meet CPE, fee and ethics requirements.
ISACA currently requires at least three years of professional work experience across at least two of the four CRISC domains. The qualifying experience must have been earned within the ten years before the certification application, and the certification application must be submitted within five years of passing the exam. Experience is verified as part of the application process. ISACA makes the final determination.
Official reference: Get CRISC Certified.
CRISC Course Fees vs Official ISACA Costs
There are two separate cost paths. This makes it clear what you pay EduDelphi for and what you pay directly to ISACA.
CRISC preparation packages from A$750
Selected packages can include 38+ live guided hours, LMS, recordings, 3,000+ resources, multiple mocks, study guides, revision and direct support.
Your written quotation confirms GST treatment, delivery mode, access and every training inclusion.
Official exam and certification charges
Exam registration, certification application and annual maintenance charges are controlled by ISACA.
EduDelphi does not set official ISACA fees.
| Current ISACA-published item | Member | Non-member |
|---|---|---|
| CRISC examination | US$575 | US$760 |
| Certification application | US$50 | US$50 |
| Annual certification maintenance | US$45 | US$85 |
Official pricing can change. Verify current fees with ISACA before payment. Static AUD conversions are not shown because exchange rates move.
Recommended CRISC Study Plan for Working Professionals
A strong CRISC plan builds domain knowledge first, then progressively increases scenario complexity, integration and timed practice.
Learn the domains
Use live teaching and the LMS to understand governance, risk assessment, response, reporting and controls.
Practise by domain
Work through targeted questions and review every reasoning error.
Integrate risk scenarios
Practise decisions involving ownership, evidence, treatment, KRIs and control design.
Complete timed mocks
Use final mock exams, weak-domain revision and exam strategy before the PSI appointment.
How CRISC Knowledge Applies in Australian Technology-Risk Roles
The CRISC examination is global. EduDelphi uses selected Australian contexts to help learners connect the syllabus with the governance, risk and control environments they may encounter locally.
- APRA-regulated sectors: CPS 234 information-security risk and CPS 230 operational risk, resilience and service-provider context.
- Privacy and breach response: Privacy Act and Notifiable Data Breaches context for risk and control decisions.
- Critical infrastructure: SOCI Act risk-management, resilience and third-party considerations.
- Government environments: ASD Information Security Manual and Essential Eight / evolving Essentials context.
- Cloud and third parties: concentration risk, supplier assurance, contracts, evidence and ongoing monitoring.
- Executive reporting: KRIs, thresholds, escalation and clear risk recommendations for decision makers.
CRISC Career Paths in Australia
CRISC knowledge is relevant where professionals must connect technology and security issues with business risk, controls, governance and reporting.
- Technology Risk Analyst or Manager
- Cyber Risk or GRC Professional
- IT Risk and Controls Manager
- Third-Party Risk Specialist
- Technology Assurance Consultant
- Security Governance Professional
- Operational Resilience or Control Lead
CRISC vs CISM vs CISA vs CISSP
| Credential | Typical career alignment | Primary emphasis |
|---|---|---|
| CRISC | Technology-risk, cyber-risk, GRC and controls professionals | Risk identification, assessment, response, reporting and controls |
| CISM | Security managers and program leaders | Security governance, programs, risk and incidents |
| CISA | IT audit and assurance professionals | Auditing information systems and controls |
| CISSP | Experienced cybersecurity professionals | Broad security architecture, engineering and management knowledge |
No credential is universally better. Choose according to the work and responsibility you want. CRISC is the most directly focused of these routes on enterprise IT risk and information-systems controls.
Meet Your CRISC Trainer
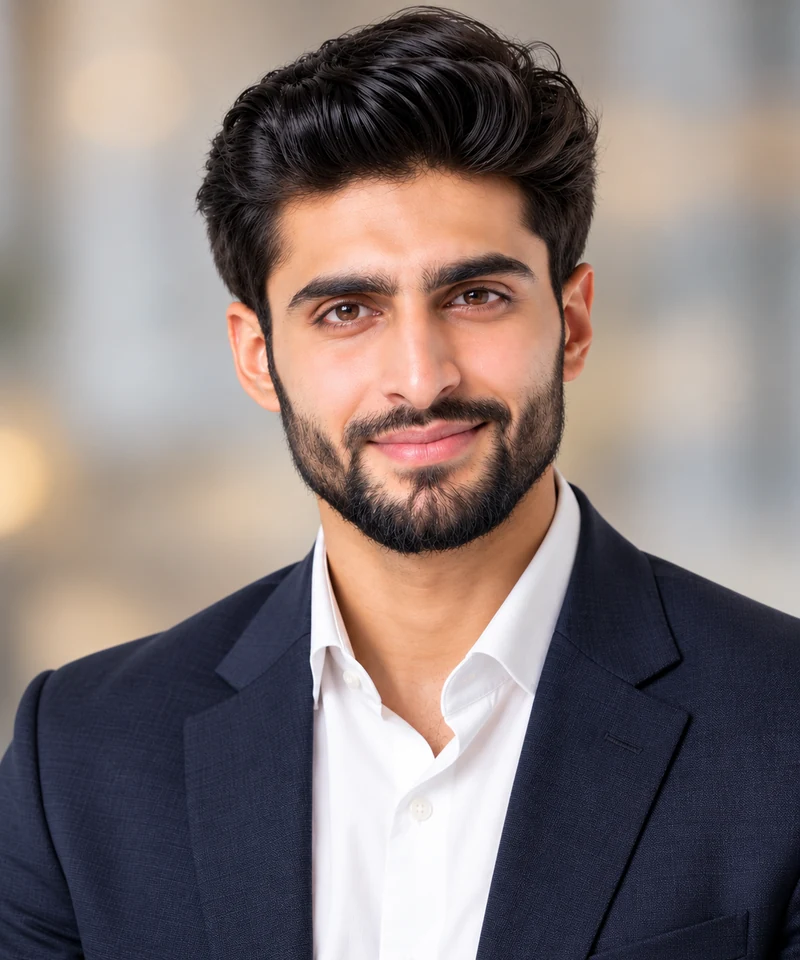
Kashif Akhtar
CISA, CISM, CRISC, CDPSE, PMP, CSCP | Qualified Engineer
Kashif brings 30+ years of practical experience across IT risk, cybersecurity, technology governance and enterprise systems, together with 13+ years of professional certification training.
For Australian CRISC candidates, he connects risk identification, assessment, treatment, controls, KRIs, third-party risk, cyber resilience and governance with realistic enterprise scenarios. His teaching is strongly exam-focused, helping learners master ISACA question logic, risk-based judgement, prioritisation and management-level decision-making rather than relying on memorisation.
What EduDelphi Learners Say
Institution-wide learner feedback on teaching quality, practical explanation and support across EduDelphi professional training.
“Good diverse classmates, some experienced and some learning. I liked the combination of practical notes and explanation of why something is important, not just how to do it.”
“Great experience in learning with Delphi, very professional staff, detailed training, and a strong overall learning environment.”
“Simple and logical explanations helped me understand the concepts and apply them in exam questions. The trainers have excellent practical knowledge.”
Corporate CRISC Training for Australian Risk & Security Teams
Build a shared approach to technology risk, controls, KRIs and reporting through private CRISC preparation for your organisation.
- Live online, classroom, hybrid and onsite delivery
- Scheduling around operational commitments
- Sector-relevant risk and control scenarios
- LMS, recordings, practice resources and mocks
- Private cohorts and direct trainer support
- Attendance and learning documentation where agreed
Live Online, Classroom, Private & Corporate CRISC Training
Live online CRISC preparation is available nationwide, including Sydney, Melbourne, Brisbane, Perth, Adelaide, Canberra and regional Australia. Classroom, private and onsite delivery can be arranged subject to cohort, location and scheduling requirements.
Live online
Instructor-led classes with interaction, recordings and direct support.
Classroom
Face-to-face delivery can be arranged according to cohort and location needs.
Private
One-to-one or tailored preparation around an individual target date.
Corporate
Private team delivery online, onsite or in a hybrid format.
Maintaining the CRISC Certification
After certification, CRISC is maintained through continuing professional education, annual reporting and compliance with ISACA requirements.
20 CPE annually
Report at least 20 continuing professional education hours each year.
120 CPE over three years
Meet the minimum across each three-year reporting cycle.
Fees and ethics
Pay the annual maintenance fee and comply with ISACA’s professional ethics requirements.
Verify current rules through ISACA’s CRISC maintenance guidance.
CRISC Course & Certification FAQs
1. What is CRISC certification?
CRISC is ISACA’s Certified in Risk and Information Systems Control credential. It focuses on governance, risk assessment, risk response and reporting, and technology and security controls.
2. Is CRISC suitable for beginners?
You can begin learning and take the exam before meeting the full experience requirement, but CRISC is a professional risk-and-controls credential. Exposure to IT, cybersecurity, audit, governance, risk or controls is helpful.
3. Can I take the CRISC exam before I have three years of experience?
Yes. Exam eligibility and certification eligibility are separate. You can pass the exam first and later meet ISACA’s current experience and application requirements.
4. How many questions are in the CRISC exam?
The official CRISC examination contains 150 multiple-choice questions and allows four hours.
5. What is the CRISC passing score?
ISACA reports scores on a 200–800 scale. A scaled score of 450 or higher is required. It is not a raw percentage.
6. Can I take the CRISC exam online from Australia?
Yes. ISACA currently offers CRISC through authorised PSI test centres and remote proctoring, subject to appointment availability, identity requirements, system compatibility and testing-environment rules.
7. What are the current CRISC domain weights?
Governance 26%, Risk Assessment 22%, Risk Response and Reporting 32%, and Technology and Security 20% under the current official outline.
8. How much does the official CRISC exam cost?
Current ISACA-published pricing is US$575 for members and US$760 for non-members. Verify the live price with ISACA before payment.
9. Is the exam fee included in EduDelphi tuition?
No. The official CRISC examination fee is paid separately to ISACA unless a specific written corporate or promotional offer explicitly states otherwise.
10. How long should I study for CRISC?
The right duration depends on your experience, weekly capacity and target date. EduDelphi uses 38+ guided hours plus structured practice, mocks and revision; flexible routes can adapt the sequence.
11. Is CRISC better than CISM or CISA?
No credential is universally better. CRISC aligns most closely with technology risk and controls, CISM with security management, and CISA with IT audit and assurance.
12. What happens if I do not pass?
ISACA currently permits up to four attempts in a rolling 12-month period, with a 30-day wait before attempt two and 90-day waits before the next permitted attempts. A new exam fee applies each time.
13. Does EduDelphi issue CRISC certification?
No. ISACA awards CRISC. EduDelphi provides independent training, practice, mocks, study support and official-process guidance.
14. Can EduDelphi train a corporate team?
Yes. Private live online, classroom, hybrid and onsite routes are available for Australian organisations.
Get CRISC Course Fees & the Next Australian Batch
Request the current syllabus, AUD package guidance and the delivery route that fits your target exam date.
- Packages from A$750
- 38+ guided live hours
- 3,000+ practice resources and questions
- Live online, classroom, private and corporate options
- Evening and weekend availability
Speak with EduDelphi Australia
Phone: +61 4 8598 4141
Email: [email protected]
Australia office: MacArthur Ave, Hamilton QLD 4007
Your written quotation confirms package inclusions and GST treatment. Official ISACA charges remain separate unless stated in writing.