CISA Course in Oman for Technology Audit Professionals
Prepare for ISACA’s Certified Information Systems Auditor® (CISA®) exam through 40+ live guided hours, structured teaching across all five domains, 3,000+ practice questions, timed mocks, recordings and an advanced revision system.
EduDelphi provides CISA training, practical IT-audit learning and candidate guidance. ISACA controls the official exam, experience assessment, certification award and maintenance requirements.
CISA Course Snapshot
- 40+ live guided training hours
- Muscat classroom, live online, private, self-paced and corporate routes
- 3,000+ questions with domain diagnostics and mixed practice
- Timed domain assessments and multiple full-length mock exams
- Full exam simulation, mock debriefs and distractor analysis
- Recordings, notes, mind maps, checklists and AI-supported LMS tools
- ISACA exam, experience, application and certification guidance
- Career support and an EduDelphi course completion certificate
live guided hours
current CISA domains
practice questions
official exam questions
official passing score
Live CISA Training in Muscat and Across Oman
Choose a route that fits your workload without reducing preparation depth. Join through Muscat classroom sessions, live online classes, private or one-to-one preparation, self-paced support, blended learning or an employer cohort.
- Flexible weekday, evening and weekend scheduling
- Live faculty teaching with class recordings
- Private and one-to-one preparation
- Classroom support in Muscat
- Live online access across Oman
- Custom onsite corporate delivery nationwide
- Revision support after the guided classes
Professionals can prepare from Muscat, Sohar, Salalah, Nizwa, Duqm and other locations throughout Oman.
What Is CISA Certification?
CISA is ISACA’s Certified Information Systems Auditor credential for professionals who audit, assess, govern and help protect information systems.
EduDelphi CISA Course
Live training, question practice, mocks, LMS resources, practical audit scenarios and candidate support.
ISACA CISA Exam
A 150-question, four-hour professional examination testing five current job-practice domains.
CISA Certification
Awarded by ISACA after the candidate passes the exam and meets current experience, application and professional requirements.
Who Should Take the CISA Course in Oman?
IT Auditors
Develop stronger audit planning, evidence, testing, reporting and follow-up judgement.
Internal Auditors
Build confidence when reviewing applications, infrastructure, access, projects and cyber controls.
Technology Risk and GRC
Connect governance, risk ownership, control design, monitoring and assurance.
Cybersecurity Professionals
Learn how an auditor evaluates protection, incidents, vulnerabilities and information assets.
IT Managers
Understand the evidence, governance and control expectations used in independent assurance.
Compliance and Assurance
Assess whether technology-related obligations are translated into reliable controls.
Consultants
Strengthen technology-control reviews, risk assessments and audit recommendations.
Early-Career Candidates
Build exam knowledge and a practical foundation while progressing towards eligible experience.
CISA is usually strongest for candidates pursuing information-systems audit, technology assurance, cyber audit, IT controls, technology risk or governance responsibilities. It is not necessary for every general IT or cybersecurity role.
EduDelphi CISA LMS and Revision System
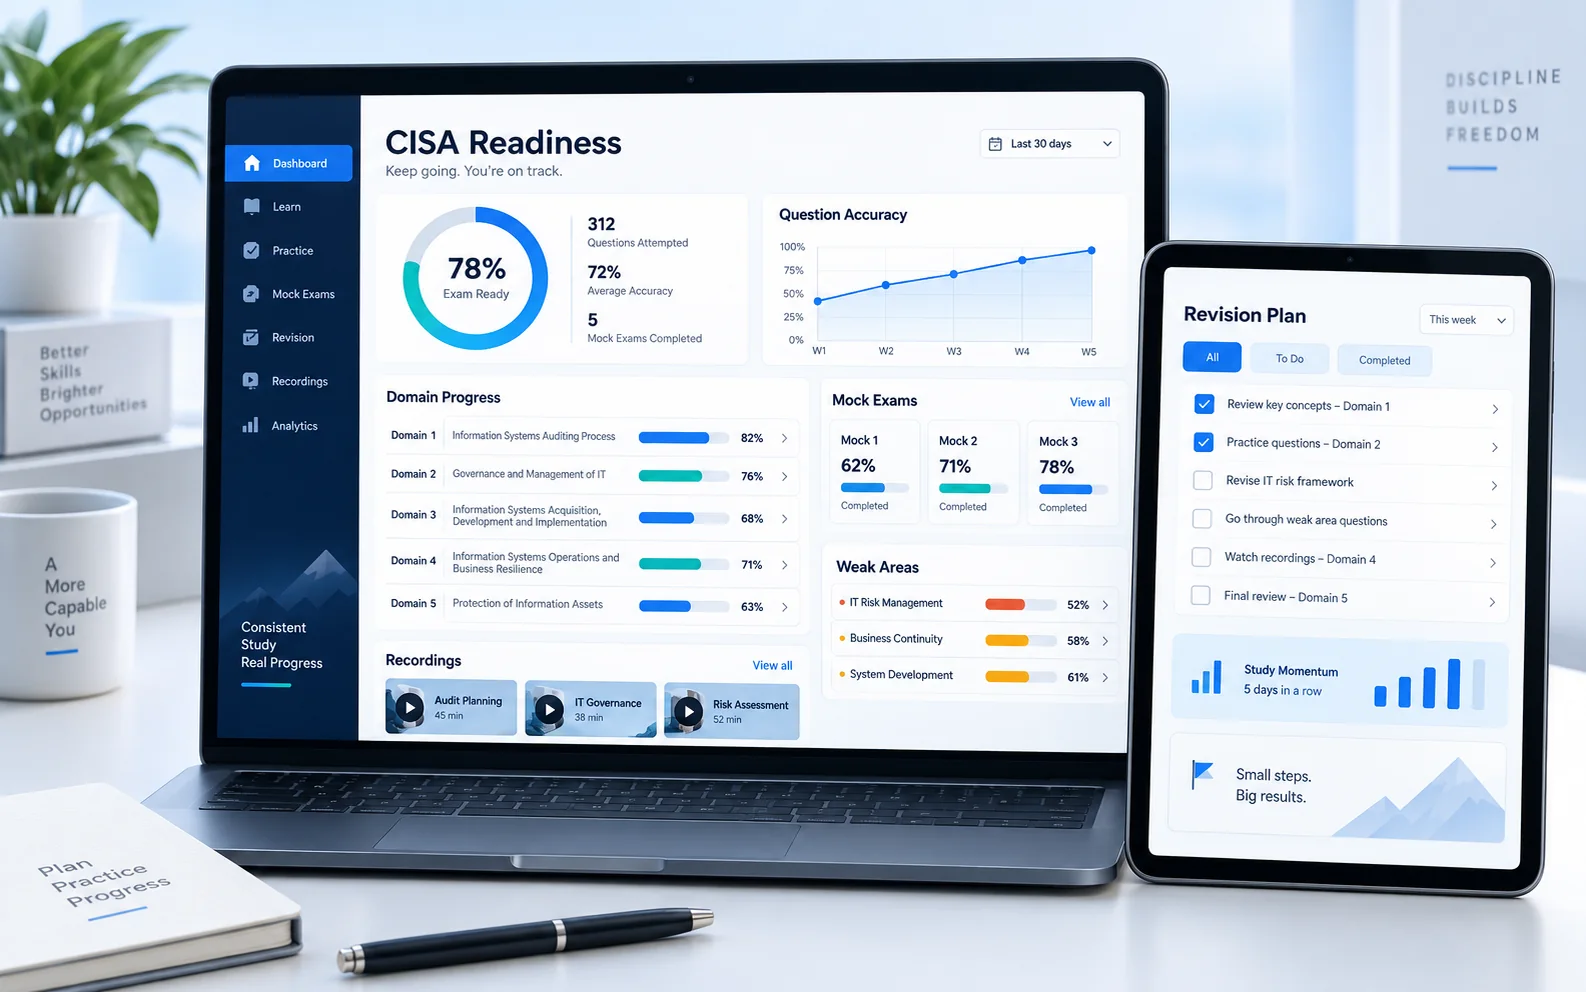
The guided classes are reinforced through a learning system that turns practice data into a focused revision plan.
Revisit complete sessions and difficult explanations.
Track completion and readiness across all five domains.
Review accuracy, speed, confidence and repeat errors.
Compare timed attempts and identify performance trends.
Use concise revision resources for rapid recall.
Connect risk, controls, evidence and conclusions.
Search learning resources and clarify difficult concepts.
Prioritise weak areas before repeating tests.
From Domain Questions to Full CISA Exam Simulation
Practice is structured as a progression. Candidates first diagnose knowledge gaps, then develop judgement, integrate domains and finally work under full exam conditions.
Domain Diagnostics
Establish the starting point and identify where prior experience does or does not transfer to CISA.
Topic-Wise Practice
Build control, governance, evidence and technology knowledge in manageable sets.
Timed Domain Tests
Measure accuracy and pacing across the current domain structure.
Mixed-Domain Drills
Practise recognising which principle a scenario is actually testing.
Full-Length Mocks
Complete multiple timed mock exams using a realistic exam rhythm.
Answer Debriefs
Understand why the best audit answer is stronger than plausible alternatives.
Error Diagnosis
Separate concept, interpretation, judgement, ownership, evidence and timing mistakes.
Retest and Readiness
Revise weak areas, retest them and compare performance before the target appointment.
The system includes 3,000+ questions, domain diagnostics, topic practice, timed assessments, multiple full mocks, exam simulation, question explanations, faculty review, mock analysis, error logs, weak-area plans, repeat testing and final exam strategy.
CISA Syllabus and Five Exam Domains
EduDelphi aligns the course to the current official CISA exam content outline. Domain 4 and Domain 5 together represent 52% of the examination.
The current CISA Exam Content Outline became effective on 1 August 2024 and remains active in 2026. If a book, question bank or provider shows weights other than 18% / 18% / 12% / 26% / 26%, confirm that the material has been updated before relying on it.
D2: Governance & Management of IT
D3: IS Acquisition, Development & Implementation
D4: IS Operations & Business Resilience
D5: Protection of Information Assets
Domain 1: Information Systems Auditing Process — 18%
Planning: IS audit standards, guidelines and ethics; types of audits, assessments and reviews; risk-based audit planning; controls and control considerations.
Execution: audit project management; testing and sampling; evidence collection; audit data analytics; reporting and communication; quality assurance and improvement.
EduDelphi application: scoping an audit, identifying control objectives, selecting evidence, evaluating findings and choosing the auditor’s most appropriate next action.
Domain 2: Governance & Management of IT — 18%
IT governance: laws and standards; organisational structure; IT strategy; policies and procedures; enterprise architecture; enterprise risk; privacy; data governance and classification.
IT management: resource management; vendor management; performance monitoring; quality assurance and quality management.
EduDelphi application: governance ownership, three-lines responsibilities, KPIs and KRIs, third-party oversight, policy effectiveness and alignment between technology and business objectives.
Domain 3: Information Systems Acquisition, Development & Implementation — 12%
Acquisition and development: project governance, business cases, feasibility, systems-development methods and control design.
Implementation: readiness testing, configuration, release management, migration, infrastructure deployment, data conversion and post-implementation review.
EduDelphi application: determining when auditors should become involved, reviewing stage gates, assessing testing evidence, evaluating migration controls and identifying independence risks.
Domain 4: Information Systems Operations & Business Resilience — 26%
Operations: IT components; assets; scheduling and automation; interfaces; shadow IT; capacity and availability; incident and problem management; change, configuration and patch management; logs; service levels; databases.
Business resilience: business-impact analysis; operational resilience; backup, storage and restoration; business-continuity and disaster-recovery plans.
EduDelphi application: audit evidence for availability, batch processing, incident response, backups, recovery testing, privileged operations, change approvals and service-provider performance.
Domain 5: Protection of Information Assets — 26%
Security and control: frameworks and standards; physical and environmental controls; identity and access; network and endpoint security; data-loss prevention; encryption; PKI; cloud; virtualisation; mobile, wireless and IoT.
Security events: awareness; attack methods; security testing; monitoring; incident response; evidence collection and forensics.
EduDelphi application: evaluating preventive, detective and corrective controls; access recertification; cloud responsibilities; vulnerability management; incident evidence and security-program assurance.
CISA Exam Format, Passing Score and Results
| Exam item | Current official position | How EduDelphi prepares you |
|---|---|---|
| Questions | 150 multiple-choice questions | 3,000+ questions, mixed-domain practice and multiple full mocks |
| Duration | Four hours | Timed tests, pacing analysis and complete simulation |
| Scoring | Scaled score from 200 to 800 | Readiness is monitored through trend and error analysis, not a false score guarantee |
| Pass score | 450 | Build consistent domain knowledge and scenario judgement |
| Incorrect answers | No penalty; answer every question | Use elimination and decision logic when certainty is incomplete |
| Delivery | PSI test centre or remote proctoring, subject to live requirements and availability | Registration, scheduling and exam-process guidance |
| Results | Preliminary status after completion; official result generally within ten working days | Post-exam certification-path guidance |
| Eligibility period | Six months after exam registration | Schedule registration around realistic readiness |
| Registration and scheduling | Year-round registration; earliest appointment 48 hours after payment; appointments visible up to 90 days ahead | Plan the registration date, target appointment and study milestones together |
| Rescheduling | No penalty when changed at least 48 hours before the appointment | Confirm the live PSI appointment terms before making a change |
ISACA reports exam performance on a 200–800 scaled range. A scaled score of 450 is the minimum passing standard and should not be converted into a raw percentage. There is no penalty for an incorrect answer, so answer every question.
Anyone may register for and sit the exam. Passing it does not by itself award the CISA certification; the separate experience and application requirements still apply.
How the CISA Exam and Certification Journey Works
Review background, target date and delivery route.
Study five domains and complete structured practice.
Pay ISACA and schedule through the available PSI route.
Complete the 150-question examination.
Document qualifying experience and submit the certification application.
Meet annual fees, ethics and CPE requirements.
EduDelphi supports exam registration, appointment planning, fee guidance, experience-waiver planning, application preparation and maintenance awareness. ISACA makes all final exam and certification decisions.
CISA Experience Requirements Explained
CISA certification normally requires five years of qualifying information-systems auditing, control, assurance or security experience. Current ISACA waiver rules can reduce the requirement by up to three years, but at least two years must remain actual CISA-domain experience. The qualifying work claimed must fall within the ten years preceding the certification application.
| Background | Potential waiver | Important condition |
|---|---|---|
| General audit or general information-systems work | 1 year | At least one year is required, and the same employment dates cannot also be claimed as CISA-domain experience |
| Associate degree | 1 year | Documentary evidence is required |
| Bachelor’s, master’s or doctoral degree in any field | 2 years | Not restricted to an IT degree |
| Master’s degree in information systems or a related field | 3 years | Maximum education waiver route currently listed |
| Full CIMA certification | 2 years | Subject to documentary verification |
| ACCA member status | 2 years | Subject to documentary verification |
Apply Within Five Years
A successful exam candidate must submit the CISA certification application within the current five-year period after passing.
Ten-Year Recency Rule
The qualifying work claimed must have been gained within the ten years preceding the certification application.
Who Can Verify Experience?
A supervisor, manager, colleague or client who knows the work may verify it. Immediate or extended family and HR personnel cannot serve as the verifier.
Final eligibility and waiver decisions are controlled by ISACA. See the current CISA certification application.
CISA Course Fees in Oman and Official ISACA Charges
EduDelphi tuition is quoted in OMR. ISACA exam, application, membership and maintenance charges are separate unless a written quotation explicitly says otherwise.
EduDelphi CISA Tuition
Tuition is enquiry-led and depends on the selected learning route, active batch and included support.
- 40+ live guided hours
- Recordings and advanced LMS resources
- 3,000+ questions, diagnostics and domain tests
- Multiple full mocks and exam simulation
- Practical audit cases and question debriefs
- Registration, certification and career guidance
Current ISACA Cost Reference
| Official item | Member | Non-member |
|---|---|---|
| CISA exam | US$575 | US$760 |
| Certification application | US$50 | US$50 |
| Annual certification maintenance | US$45 | US$85 |
Membership and other optional or situational charges can apply. The full exam registration fee must be paid again for every retake. Official amounts may change, so candidates should verify them before payment.
CISA Skills in Oman’s IT Audit and Technology-Risk Environment
CISA is an international professional certification rather than an Oman occupational licence. Its subject matter is nevertheless directly relevant wherever organisations depend on governed, resilient and securely controlled technology.
Banking and Financial Services
Core systems, privileged access, change management, cyber controls, third parties, resilience and regulatory assurance.
Oil, Gas and Utilities
Operational technology interfaces, vendor dependencies, continuity, asset governance and enterprise-system controls.
Telecom and Digital Services
Availability, capacity, identity, networks, incident response, privacy, cloud and information-asset protection.
Government and Public Services
Technology governance, data classification, security assessment, system implementation and service resilience.
Logistics and Large Corporates
ERP access, interfaces, automated jobs, databases, third parties, project controls and disaster recovery.
Audit and Advisory Firms
IT general controls, technology assurance, cyber audit, systems reviews and evidence-based recommendations.
Oman has an active ISACA Muscat Chapter. Current Omani technical standards also reference CISA within selected audit, risk-assessment and information-security capability contexts. This supports professional relevance; it does not create a universal licence or guarantee employment.
Explore the ISACA Muscat Chapter and Oman MTCIT’s Security Assessment Services Standard.
Learn CISA with Kashif Akhtar
Kashif Akhtar
CISA | CISM | CRISC | CDPSE | PMP | CSCP | Qualified Engineer
30+ Years in Technology, IT Audit, Cyber Risk & Enterprise Systems | 13+ Years in Professional Certification Training
Kashif brings 30+ years of practical experience across technology, IT audit, cybersecurity, governance, risk and enterprise systems, including senior exposure within multinational and complex operating environments. He has worked closely with IT leadership, internal audit, information security, risk, operations and senior management teams, giving him a strong practitioner perspective on how technology controls are designed, tested and governed.
For CISA learners in Oman, Kashif connects ISACA concepts with practical environments across banking, oil & gas, telecom, utilities, logistics, government-linked organisations and large corporate groups. His sessions cover IT audit planning, governance, systems acquisition and implementation, IT operations, business continuity, access management, cybersecurity, third-party risk and control assurance.
With 13+ years of certification training experience, Kashif is particularly strong at ISACA-style scenario questions. He helps candidates identify what the question is really testing, determine the auditor’s best next action, distinguish between technically correct and audit-appropriate answers, and understand the logic around risk, evidence, ownership, materiality and control effectiveness.
His classes combine real enterprise scenarios, audit cases, control reviews, topic-wise question practice, mock analysis and targeted revision, helping Oman-based professionals build both practical IT-audit judgement and strong CISA exam technique.
How We Teach CISA Audit Judgement
A company has moved a critical finance application to a cloud provider. Management provides the vendor’s security certification, a service-level report and a summary of user-access reviews. The auditor learns that privileged-access logs are retained by the vendor, but the company has never requested or reviewed them. A system administrator recently left the company, and management cannot demonstrate when the vendor removed that account.
Candidate Tasks
- Identify the most significant audit concern.
- Determine which evidence the auditor should obtain next.
- Assess whether the vendor certificate is enough.
- Distinguish design, operation and oversight weaknesses.
- Recommend a proportionate corrective action.
CISA Thinking Sequence
Control objective
Expected control
Evidence
Design
Operation
Finding
Recommendation
The strongest conclusion is not simply that “the cloud provider is risky.” Management retains responsibility for access governance and service-provider oversight. The auditor should obtain evidence of account deprovisioning, privileged-access activity and management’s monitoring of the provider. A third-party assurance report may inform the audit, but it does not prove that the organisation’s own user-management and oversight controls operated effectively.
The example integrates Domain 1 audit evidence, Domain 2 governance and vendor management, Domain 4 operations and Domain 5 access protection.
Original EduDelphi practice scenario. This is not an official, recalled or live CISA examination question.
How to Use the 40+ Live Hours Effectively
Before Class
Review the topic map, baseline questions and assigned concepts.
During Class
Work through principles, practical cases and ISACA-style decisions with faculty.
After Class
Use recordings, notes, questions and the error log to reinforce the topic.
Before the Exam
Complete domain tests, mixed practice, full mocks, remediation and final simulation.
Preparation time outside the guided hours depends on prior experience, reading speed, technical background, target date and practice performance. EduDelphi builds a personal plan around the learner rather than promising the same preparation time for every candidate.
CISA-Aligned Roles and Career Support in Oman
CISA knowledge can strengthen a profile for technology-audit, governance, controls and assurance work. The certification does not guarantee a role or salary, and employer requirements vary.
IT Audit
IT Auditor, Senior IT Auditor, IT Audit Manager and systems-assurance roles.
Technology Risk
Technology Risk Analyst, Risk Manager and third-party technology-risk roles.
GRC and Controls
GRC Analyst, IT Controls Specialist, governance and compliance roles.
Cyber Assurance
Cybersecurity Auditor, security-assurance consultant and control-assessment roles.
Support can include CV improvement, LinkedIn optimisation, role mapping, job-application guidance, interview preparation, recruiter outreach and access to the wider alumni ecosystem. The goal is to help candidates present their actual experience and developing CISA capability credibly.
CISA vs CISM, CRISC, CISSP and CIA
| Credential | Core focus | Commonly aligned roles | Useful next step |
|---|---|---|---|
| CISA | Information-systems audit, technology controls, governance, operations, resilience and information assets | IT audit, technology assurance, cyber audit and GRC | Current page |
| CISM | Information-security management, governance, programme development and incident oversight | Security managers and information-security leaders | Explore CISM training |
| CRISC | Enterprise IT risk and information-systems controls | Technology risk, control ownership and risk advisory | Discuss the right ISACA route |
| CISSP | Broad cybersecurity architecture, engineering, operations and management | Experienced cybersecurity professionals | Read CISA vs CISSP |
|
CIA |
Internal audit across governance, risk, controls and business processes | Internal audit and assurance | CIA course in Oman |
The credentials can complement one another. Choose according to the work you perform or want to perform, not solely by comparing acronym popularity.
What CISA Learners Say
“Staff is professional and humble. Knowledgeable faculty. Flexible approach and certainly good choice. I would recommend approaching Delphi Star Training Centre for necessary coaching and guidance.”
Bhavin Raithatha
CISA learner
“This institute is one of the best institutes which provides training in CISA. The trainer is highly experienced. I gained a lot of knowledge in CISA. Thanks to DELPHI.”
Rashid Humaid Al Badi
CISA learner
“Good training by a knowledgeable instructor and supported by appropriate facilities.”
Mobbashar Khan
CISA learner
Corporate CISA and IT Audit Training in Oman
EduDelphi supports internal audit, technology, cybersecurity, risk and governance teams through private CISA cohorts and wider IT-audit capability programmes.
- Private CISA examination-preparation cohorts
- Pre-programme capability assessment
- Role-based learning paths and custom schedules
- Organisation-specific audit and control scenarios
- IT audit planning, evidence, findings and reporting
- Access governance, change management and systems implementation
- Cloud, third-party and cybersecurity control assurance
- Business-continuity and disaster-recovery reviews
- Attendance, participation, progress and readiness reporting
- Private recordings where contractually agreed
- Dedicated programme coordination, PO and invoicing support
- Muscat, workplace, off-site, live online and nationwide delivery
Employers can also commission practical capability programmes in IT governance, technology risk, cybersecurity audit and IT controls without requiring every participant to register for the CISA exam.
CISA Guides and Related Oman Courses
Requirements and Exam
Read the detailed guides to CISA requirements, exam format and domains, and exam difficulty.
Cost and Study Planning
Explore the CISA cost guide, study-duration guide and first-attempt preparation system.
Audit, Fraud and Compliance
Compare the CIA course, CFE course and CAMS course in Oman.
Candidates seeking a country-neutral programme can review the global online CISA course. Browse all EduDelphi courses in Oman.
EduDelphi Oman Course Support in Muscat
Speak with the Muscat team about CISA delivery, current OMR tuition, flexible batches, exam planning, private preparation or employer training.
EduDelphi Muscat Office
Street 3701, Al Ghubrah South
Postal Code 130, Muscat, Oman
Phone and WhatsApp
+971 52 908 6650
Prepare from Anywhere in Oman
Join live online from Muscat, Sohar, Salalah, Nizwa, Duqm and other locations. Classroom, private and employer delivery can be planned around the selected format.
CISA Course Oman FAQs
What is CISA certification?
CISA is ISACA’s Certified Information Systems Auditor credential. It validates knowledge across information-systems auditing, IT governance, systems development, IT operations, resilience and information-asset protection.
Who awards the CISA certification?
ISACA controls the CISA exam and awards the certification after the candidate meets its current exam, experience, application and professional requirements. EduDelphi provides independent training and preparation support.
Can I take the CISA exam without five years of experience?
Yes. Anyone may register for and sit the examination. The experience requirement applies when applying for the full CISA certification after passing.
How much experience is required for CISA certification?
Current guidance generally requires five years of relevant information-systems auditing, control, assurance or security experience. Waivers may reduce up to three years, leaving at least two years of actual CISA-domain experience.
Can my degree reduce the CISA experience requirement?
Yes. Current guidance allows education waivers including one year for an associate degree, two years for a bachelor’s, master’s or doctorate in any field, and up to three years for a qualifying master’s in information systems or a related field. ISACA makes the final decision.
What is the CISA exam format?
The current CISA exam contains 150 multiple-choice questions completed in four hours. Questions cover five job-practice domains.
What score is required to pass CISA?
The passing score is 450 on ISACA’s scaled range of 200 to 800. It should not be interpreted as a simple percentage.
Is there negative marking on the CISA exam?
No. Current ISACA guidance does not apply a penalty for incorrect answers, so candidates should answer every question.
How long do I have to take the exam after registration?
Current CISA exam eligibility lasts six months from registration. Candidates should register when their preparation and intended appointment are reasonably aligned.
Can I take the CISA exam online from Oman?
ISACA currently delivers CISA through authorised PSI test centres and remote proctoring. The routes shown to an individual candidate depend on current technical, identity, location and appointment availability, so check the live scheduling system before finalising plans.
Is CISA here the ISACA certification or the U.S. agency?
This page covers ISACA’s Certified Information Systems Auditor® (CISA®) certification.
How much does the CISA exam cost?
Current official reference pricing is US$575 for an ISACA member and US$760 for a non-member. The certification application is currently US$50 after passing. EduDelphi tuition is separate and quoted in OMR.
When will I receive my CISA result?
Candidates normally see a preliminary status after completing the exam. ISACA currently states that official results are emailed and posted within ten working days.
What happens if I do not pass CISA?
ISACA currently permits four attempts within a rolling 12-month period. After the first unsuccessful attempt, candidates wait 30 days before attempt two; after attempts two and three, the waiting period is 90 days before the next permitted attempt. Each attempt requires a new exam registration fee.
What is CISA Associate?
CISA Associate is a separate ISACA designation for eligible students participating through the applicable partner-program route who pass the CISA exam before completing the work experience required for full CISA certification. It is not automatically awarded to every candidate who passes without experience.
How many CPE hours are required after certification?
Current maintenance rules require at least 20 CPE hours each year and 120 hours across each three-year reporting cycle, together with applicable fees and professional requirements.
How long does CISA preparation take?
EduDelphi provides 40+ live guided hours plus recordings, practice, mocks and revision. Total preparation time varies according to audit experience, technical background, weekly availability and performance in questions.
Is the CISA exam available in Arabic?
Arabic is not currently listed among the official CISA exam languages. Arabic or bilingual teaching support can be discussed separately for a selected EduDelphi batch or private programme.
Is CISA recognised in Oman?
CISA is an international professional certification rather than an Oman occupational licence. Its audit and control capabilities are relevant to many local technology-risk and assurance environments, and selected Oman technical standards reference CISA in specialist competency contexts.
Does EduDelphi provide corporate CISA training in Oman?
Yes. Private CISA cohorts and customised IT-audit capability programmes can be delivered live online, in Muscat, at an employer workplace or at an agreed location across Oman.
What do I receive after completing the EduDelphi course?
Eligible completers receive an EduDelphi CISA Course Completion Certificate. This confirms course completion and is separate from the CISA certification awarded only by ISACA.
Official requirements can change. Verify current exam, fee, experience and maintenance information directly with ISACA.
Get CISA Fees, Syllabus and Oman Batch Options
Tell us your experience, preferred format and target exam period. We will send the current OMR tuition and a practical preparation plan.
- 40+ live guided hours and flexible delivery
- Muscat classroom, live online, private and corporate options
- 3,000+ questions, domain tests, mocks and full simulation
- Recordings, LMS resources, revision and faculty guidance
- ISACA exam, experience and certification-process support
Start Your CISA Preparation in Oman
Get the five-domain syllabus, current official-cost guidance, OMR tuition, flexible batch options and a study route built around your background.