CISM Course in Oman for Security Leaders and Managers
Prepare for the Certified Information Security Manager® (CISM®) exam through 40+ guided live hours, structured teaching across all four domains, 3,000+ CISM practice questions, multiple timed mocks, recordings and an advanced learning system.
EduDelphi provides independent CISM training, practical security-management learning and candidate support. ISACA administers the official exam, assesses certification applications and controls the credential’s maintenance requirements.
CISM Course Snapshot
- 40+ guided live training hours
- Muscat classroom, live online, hybrid, private, self-paced and corporate routes
- Flexible weekday, weekend and fast-track batches
- 3,000+ CISM practice questions with domain diagnostics
- Multiple full-length timed mocks and exam simulations
- Recordings, notes, mind maps, flashcards and AI-supported LMS tools
- Individual doubt support, mock analysis and weak-area review
- Exam, application, career and job-search support
CISM 2026 Exam Update: Old vs New Syllabus from 3 November
ISACA changes the CISM domain weighting on 3 November 2026. EduDelphi maps your classes, question practice and revision resources to the outline that applies on your intended examination date.
Use the updated 18% / 20% / 33% / 29% blueprint. The domain names remain the same, but the revised outline expands selected information-security strategy, programme-development and architecture coverage. EduDelphi preparation for examinations from 3 November 2026 is mapped to the revised 18% / 20% / 33% / 29% outline.
ISACA released preparation materials aligned to the new outline from 1 September 2026. If your exam is on or after 3 November 2026, make sure your review manual, question resources and training plan are mapped to the revised outline rather than relying on older materials.
| Intended exam date | Governance | Risk | Security Programme | Incident Management | Materials to use |
|---|---|---|---|---|---|
| Through 2 November 2026 | 17% | 20% | 33% | 30% | Pre-update outline and matching course resources |
| From 3 November 2026 | 18% | 20% | 33% | 29% | Updated outline and exam-date-aligned resources |
Candidates should always prepare against the outline attached to their actual test date. EduDelphi independently aligns its training to current ISACA information; ISACA controls the official examination.
Keep EduDelphi Tuition Separate from ISACA Fees
Your total investment has two separate components. EduDelphi charges for training and support; ISACA controls its examination, application and maintenance charges.
EduDelphi CISM Course Fee
Course fees are enquiry-led because the amount depends on the selected live, classroom, hybrid, private, self-paced or corporate route and the current package.
- Request the current Oman tuition quote
- Receive the complete inclusion list
- Compare active schedules and delivery routes
- Understand what is—and is not—included
| Official ISACA item | Current reference |
|---|---|
| Member exam fee | US$575 |
| Non-member exam fee | US$760 |
| Certification application | US$50 |
| One six-month extension | US$75 |
| Annual maintenance — member | US$45 |
| Annual maintenance — non-member | US$85 |
| Retake | Full exam-registration fee again |
Official-fee reference checked in September 2026. Taxes, membership decisions, exchange rates and checkout totals can change; verify the live ISACA amount before payment.
Live CISM Training in Muscat and Online Across Oman
Choose a delivery route that fits your workload without reducing preparation depth. Join through Muscat classroom sessions, live online classes, hybrid learning, private or one-to-one preparation, the complete self-paced course, or an employer cohort.
- Weekday, weekend and fast-track batch choices
- Live faculty teaching supported by complete recordings
- Private and one-to-one preparation where required
- Classroom and course support from Muscat
- Live online access from anywhere in Oman
- Private onsite and virtual corporate programmes
- Repeat-session and later-batch revision support
Professionals can prepare from Muscat, Sohar, Salalah, Nizwa, Sur, Duqm and other locations throughout Oman.
What Is CISM Certification?
CISM is ISACA’s management-focused credential for professionals who govern information security, manage enterprise risk, build security programmes and lead incident management.
EduDelphi CISM Course
Independent training, question practice, mocks, LMS resources, management cases, exam guidance and learner support.
ISACA CISM Exam
A 150-question, four-hour examination testing management judgement across four current domains.
CISM Certification
Awarded by ISACA after a candidate passes the exam and meets current experience, application, ethics and maintenance requirements.
What Is Included in the EduDelphi CISM Course?
Every part of the course supports a deliberate learning loop: understand the principle, apply it to a management decision, practise questions, analyse mistakes, complete mocks and revise with evidence.
40+ Live Guided Hours
Faculty-led learning across governance, risk, programme development and incident management.
3,000+ CISM Questions
Topic drills, domain tests, mixed scenarios, timed practice and detailed review.
Multiple Full Mocks
Realistic timed examinations, exam simulations, pacing work and readiness analysis.
Advanced LMS
Recordings, resources, progress visibility, practice history and structured revision support.
High-Retention Resources
Notes, mind maps, infographics, flashcards, quick-reference sheets and study plans.
Individual Support
One-to-one doubt clarification, mock analysis and targeted weak-area review.
Repeat and Revise
Repeat relevant sessions and use later revision batches where appropriate.
End-to-End Guidance
Support around registration, scheduling, fees, application planning and professional positioning.
EduDelphi CISM LMS and Readiness System
The LMS is built to help working professionals turn activity into measurable exam readiness—not simply store videos.
How the System Builds Readiness
- Diagnose: establish domain-level strengths and gaps.
- Learn: understand the business and security-management logic.
- Apply: work through realistic management scenarios.
- Practise: answer topic, domain and mixed questions.
- Review: separate knowledge errors from judgement errors.
- Simulate: complete timed mocks and full exam simulations.
- Revise: retest weak areas against a focused plan.
From Domain Questions to Full CISM Exam Simulation
CISM questions often contain several technically plausible choices. The course teaches candidates to identify the answer that best reflects management responsibility, business alignment, risk ownership, sequencing and governance.
Domain Diagnostics
Establish the starting point and identify where experience does—or does not—transfer to the exam.
Topic Drills
Build concepts in focused sets before integrating them into longer management scenarios.
Timed Domain Tests
Measure accuracy, interpretation and pace across the applicable exam weighting.
Mixed-Domain Practice
Recognise whether a scenario is testing governance, risk, programme or incident judgement.
Multiple Full Mocks
Complete realistic timed examinations with the concentration and pacing the real exam requires.
Answer Debriefs
Understand why the best management answer is stronger than close alternatives.
Error Diagnosis
Classify errors as concept, ownership, sequencing, scope, evidence or technical bias.
Retest and Readiness
Revisit weaknesses, repeat practice and compare performance before scheduling or sitting the exam.
The system combines 3,000+ CISM questions with explanations, domain diagnostics, timed tests, multiple full mocks, exam simulations, faculty debriefs, error logs, individual weak-area review and targeted retesting.
CISM Domains and Exam Weightings
The four domains remain consistent across the November 2026 transition. The weighting depends on the examination date.
For examinations from 3 November 2026
Domain 1: Information Security Governance — 18% from 3 November 2026
Develop and maintain an information-security governance framework and supporting processes that align security strategy with organisational goals. Preparation covers enterprise governance, legal and regulatory considerations, strategy, enterprise architecture, information-security architecture, roles, responsibilities, policies, standards, executive support, organisational culture, metrics and reporting.
How we teach it: candidates work through business-alignment, policy, ownership, steering, funding and executive-reporting decisions instead of memorising governance definitions in isolation.
Domain 2: Information Security Risk Management — 20%
Identify, assess, treat, monitor and communicate information risk in line with business objectives and risk appetite. Coverage includes risk identification, threat and vulnerability context, risk assessment, controls, treatment options, third-party and cloud risk, residual-risk acceptance, monitoring, reporting and integration with enterprise risk management.
How we teach it: learners distinguish the manager’s role from technical implementation and practise selecting actions based on ownership, materiality, business impact and decision authority.
Domain 3: Information Security Program — 33%
Build, operate and improve the information-security programme. Topics include programme charter and scope, resources, architecture, controls, standards, awareness, asset classification, technology and process integration, supplier management, performance indicators, programme communications, assurance, maturity and continuous improvement.
How we teach it: candidates develop programme roadmaps, metrics, control priorities, resource decisions and reporting structures linked to business requirements.
Domain 4: Incident Management — 29% from 3 November 2026
Establish and maintain incident-management capability, including readiness, detection, classification, escalation, response, communications, recovery, evidence considerations, testing, resilience and post-incident improvement. The domain focuses on management decisions and organisational coordination rather than purely technical response actions.
How we teach it: learners use tabletop cases to decide what happens first, who should be informed, how business impact changes priorities and how lessons become programme improvements.
The applicable weighting is 17% Governance, 20% Risk, 33% Programme and 30% Incident Management. Your study plan and mock weighting will be mapped accordingly.
See How CISM Tests Management Judgement
An Oman-based enterprise is preparing to launch a customer-facing platform. A late security review identifies a material weakness in a third-party integration. The launch sponsor wants to proceed because remediation may delay a public deadline. The security team can reduce—but not eliminate—the exposure before launch.
What should the information-security manager do FIRST?
- Block the launch until the technical weakness is completely eliminated.
- Ask the security team to accept the residual risk because it owns the control.
- Quantify the business exposure, identify the appropriate risk owner and present treatment options for an informed decision.
- Escalate directly to the board before determining business impact.
Best management reasoning: C. The security manager should establish risk and business impact, make ownership and decision authority clear, and provide viable treatment options. Technical teams can recommend controls; residual business risk should be handled through the appropriate governance authority, with monitoring and a time-bound treatment plan.
Original EduDelphi practice scenario. It is not an official, recalled or live CISM examination question.
CISM Exam Format, Scheduling, Results and Retakes
Use these current ISACA reference points for planning. Confirm live policies in your ISACA account before finalising an appointment.
| Exam item | Current position | What it means |
|---|---|---|
| Format | 150 multiple-choice questions | Questions test management judgement across four domains. |
| Duration | 4 hours / 240 minutes | Build both accuracy and sustainable pacing. |
| Delivery | PSI test centre or remote proctoring | Available booking options depend on the candidate’s account and live availability. |
| Registration | Continuous / year-round | No fixed annual registration season. |
| Earliest appointment | 48 hours after payment | Subject to appointment availability. |
| Appointment visibility | Up to 90 days ahead | Future dates appear on a rolling basis. |
| Eligibility | Six months from registration | The exam must be scheduled and completed inside the eligibility period. |
| Extension | One six-month extension; currently US$75 | Subject to current candidate-guide conditions. |
| Rescheduling | No penalty at least 48 hours before | Later changes may not receive the same treatment. |
| Score | 200–800 scale; 450 passes | 450 is a scaled score, not 45% or 56.25%. |
| Preliminary passing status | Displayed after completion | This is shown before the official score is released. |
| Official score | Emailed / available online within 10 working days | The official result is posted to the candidate account. |
There is no penalty for an incorrect answer. Leaving a question unanswered cannot improve the result.
Current waiting periods are 30 days before attempt two, 90 days before attempt three and another 90 days before attempt four. ISACA currently allows four attempts in a rolling 12-month period, and the full registration fee applies to every attempt.
Passing the CISM Exam Is Not the Same as Becoming CISM-Certified
Anyone interested in information security may take the examination. Certification is awarded only after ISACA confirms the remaining experience and application requirements.
Experience Requirement
Current certification requires at least five years of professional information-security-management experience across at least three of the four CISM domains. Claimed experience must fall within the ten years before the certification application.
ISACA currently permits eligible substitutions or waivers of up to two years. The exact substitution depends on the candidate’s background and current application rules, so do not assume a reduction until the current application requirements have been checked.
Maintaining CISM
Current maintenance requirements include at least 20 CPE hours annually and at least 120 CPE hours over a three-year cycle, together with the annual maintenance fee, professional-ethics obligations and audit compliance where selected.
Passing candidates have five years from the exam date to apply for certification after completing the applicable experience requirements.
Who Should Take the CISM Course in Oman?
CISM is normally strongest for professionals who already have exposure to security, risk, audit, controls, technology leadership or programme responsibility and want to develop management-level capability.
Security Managers
Strengthen governance, programme leadership, metrics and executive communication.
GRC and Risk Professionals
Connect security risk with business objectives, ownership and treatment decisions.
IT and Cyber Managers
Move from technical delivery toward policy, oversight, funding and programme accountability.
Audit and Controls Professionals
Build the management perspective needed beyond testing and assurance.
Incident and SOC Leaders
Improve readiness, escalation, cross-functional response and post-incident governance.
Security Consultants
Advise organisations on governance, risk, programme maturity and incident capability.
Technology Leaders
Understand how security strategy supports enterprise objectives and resilience.
CISO-Track Professionals
Develop the judgement expected in senior security-management roles.
A beginner can study the syllabus and take the exam, but the CISM certification itself requires relevant professional experience.
Why CISM Is Relevant Across Oman’s Critical and Regulated Sectors
Organisations across Oman are strengthening digital services, cyber governance, risk oversight, incident readiness and security reporting. CISM’s management focus is particularly relevant where leaders must translate technical exposure into business decisions, budgets, accountability and resilience.
- Banking and financial services: governance, third-party risk, customer-data protection and incident escalation.
- Oil, gas and utilities: enterprise and operational-technology risk, resilience and critical-service continuity.
- Telecom: programme governance, supplier dependencies, infrastructure security and incident coordination.
- Government and critical infrastructure: policy, accountability, risk prioritisation and public-service resilience.
- Large enterprises and consulting: cloud risk, security metrics, assurance, transformation and board reporting.
Current Oman vacancies have referenced CISM for security-management, data-security, cyber-lead, SOC, OT-security and maturity-assessment responsibilities. Employer requirements still vary by role.
The ISACA Muscat Chapter, founded in 2000, reports more than 300 members and supports professional development around CISM, CISA, CRISC and related governance, risk and audit disciplines. EduDelphi is an independent training provider and does not represent or imply a partnership with the chapter.
Career and Professional-Positioning Support
CISM is most valuable when the credential, practical experience and professional profile tell one coherent security-leadership story.
Career Direction
Discuss target paths across security management, cyber risk, GRC, incident leadership, consulting and CISO-track roles.
CV and LinkedIn
Improve positioning around programme ownership, risk decisions, controls, metrics, incidents and stakeholder leadership.
Recruiter Outreach
Build a more disciplined process for identifying employers, approaching recruiters and managing applications.
Interview Preparation
Prepare examples that demonstrate judgement, ownership, communication and measurable security outcomes.
Application Support
Organise job searches, tailor applications and maintain follow-up across relevant opportunities.
Professional Ecosystem
Use guidance, alumni context and learning support to make better next-step decisions.
Career support strengthens preparation and professional presentation; it does not guarantee employment, promotion or compensation outcomes.
CISM vs CISA vs CISSP vs CRISC
The best route depends on the work you want to perform—not which acronym appears most often.
| Credential | Core emphasis | Usually aligned when… |
|---|---|---|
| CISM | Security governance, risk, programme and incident management | You want to lead an information-security programme. |
| CISA course in Oman | IT audit, assurance, controls and evidence | Your work is audit- and assurance-led. |
| CISSP course in Oman | Broad security architecture, engineering and operations | You need wider technical-security breadth. |
| CRISC | Enterprise IT risk and control design | Risk assessment, treatment and controls dominate your role. |
For a deeper decision, read our CISA vs CISM comparison or explore broader cyber security courses in Oman.
Learn Security Management with Kashif Akhtar
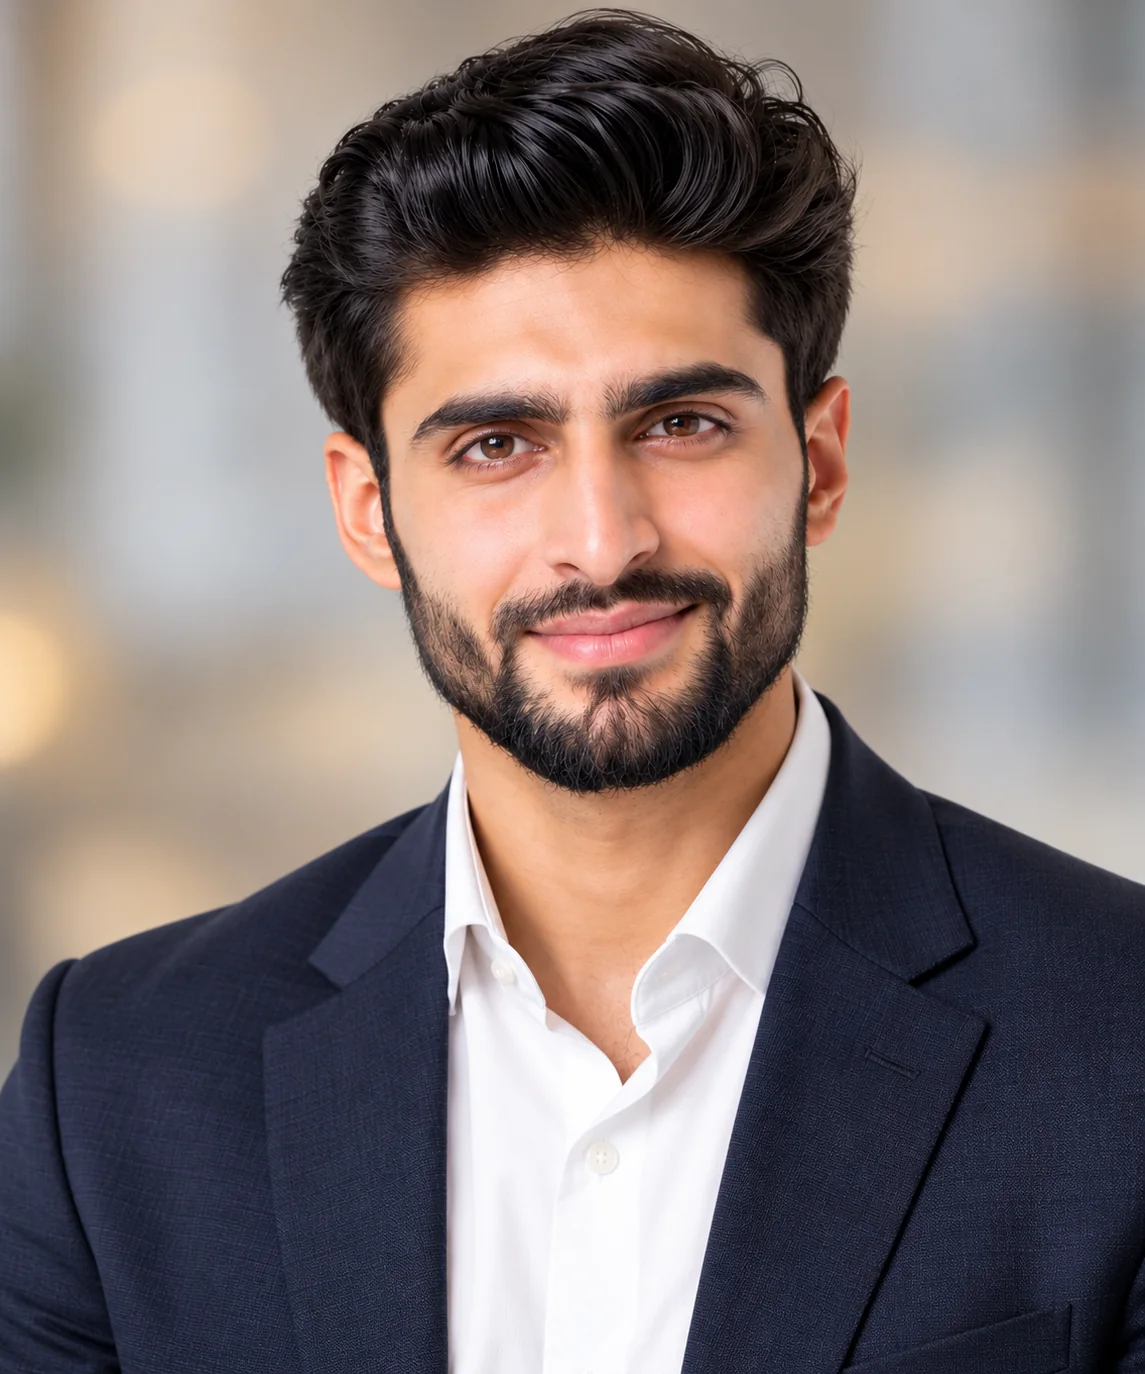
Kashif Akhtar
CISA | CISM | CRISC | CDPSE | PMP | CSCP | Qualified Engineer
30+ Years in Technology, Cybersecurity, Governance & Enterprise Risk | 13+ Years in Professional Certification Training
Kashif brings 30+ years of practical experience across technology leadership, cybersecurity, information risk, governance and enterprise systems, including senior exposure within multinational and complex operating environments. His background gives CISM learners a strong practitioner view of how security programmes are governed, funded, measured and aligned with business priorities.
For CISM learners in Oman, Kashif connects the ISACA curriculum with security challenges faced across banking, oil and gas, utilities, telecom, logistics, government-linked organisations and critical infrastructure. His sessions cover information security governance, enterprise risk management, security programme development, third-party and cloud risk, incident management, resilience, executive reporting and security performance measurement.
With 13+ years of certification training experience, Kashif is particularly strong at teaching the management mindset behind the CISM exam. Candidates learn how to identify what ISACA is really testing, determine what should happen first or next, distinguish between technical fixes and management-level responses, and understand questions around risk ownership, business alignment, policy, escalation and governance.
His classes combine real enterprise security scenarios, risk decisions, incident-response cases, governance discussions, intensive question practice and mock analysis, helping Oman-based professionals build both strong CISM exam technique and the judgement expected of senior information-security managers.
Self-Paced CISM Course and Live-Course Reinforcement
The self-paced route is available as a complete standalone product and is also used to reinforce the live course.
Standalone Self-Paced Route
Prepare through structured recorded teaching, the LMS, 3,000+ questions, study resources, domain practice, mock exams and support while managing your own timetable.
Reinforcement for Live Learners
Revisit explanations, repeat question sets, use mind maps and flashcards, analyse mocks and continue revision between live sessions.
Corporate CISM and Security-Management Training Across Oman
EduDelphi delivers private, onsite and virtual programmes for employers across Oman. A programme can combine CISM preparation with organisation-relevant work on governance, risk, programme maturity, metrics, third parties, resilience and incident readiness.
- Baseline learner and domain diagnostics
- Private schedules for working teams
- Banking, energy, telecom, government and enterprise cases
- Attendance and progress tracking
- Domain-level readiness reporting
- Mock-exam planning and faculty debriefs
- Manager-facing progress summaries
- Incident tabletop and governance exercises
Security-management capability programmes can also be scoped around risk appetite, third-party risk, programme metrics, executive reporting and incident readiness without requiring every participant to register for the CISM exam.
EduDelphi Oman — Muscat Course Support
Speak with the Oman team about CISM eligibility, schedules, tuition, delivery routes, employer programmes and the official examination process.
Street 3701, Al Ghubrah South
Postal Code 130, Muscat, Oman
Supporting Learners Across Oman
Classroom and course support is available from Muscat, while live online, private and corporate delivery serves professionals in Sohar, Salalah, Nizwa, Sur, Duqm and other locations across the country.
Request current batch options to compare weekday, weekend, fast-track, private and self-paced routes.
Frequently Asked Questions About CISM in Oman
Direct answers about the course, examination, experience, fees, scheduling and certification route.
What does CISM stand for?
CISM stands for Certified Information Security Manager. It is a professional information-security-management credential administered by ISACA.
Is CISM recognised in Oman?
CISM is an international professional certification rather than an Oman-specific occupational licence. Employers in Oman have referenced CISM for security-management, cyber-risk, SOC, data-security, OT-security and governance responsibilities. Requirements still vary by role and employer.
Who awards CISM certification?
ISACA administers the examination, assesses certification applications and awards the CISM credential. EduDelphi provides independent training and candidate support.
Can I take the CISM exam before completing five years of experience?
Yes. Anyone interested in information security may take the examination. Passing does not by itself make the candidate CISM-certified; the experience and application requirements must still be completed.
What experience is required for CISM certification?
Current certification requires at least five years of professional information-security-management experience across at least three of the four CISM domains. Claimed experience must fall within the ten years before application. ISACA currently permits eligible substitutions or waivers of up to two years. The exact reduction depends on the candidate’s background and current application rules, so do not assume it until the current application requirements have been checked.
What changes on 3 November 2026?
The weighting changes from 17/20/33/30 to 18/20/33/29 across Governance, Risk, Security Programme and Incident Management. The domain names remain the same, while the updated outline expands selected strategy, programme and architecture coverage.
How many questions are on the CISM exam?
The current CISM exam has 150 multiple-choice questions and a four-hour time limit.
What is the CISM passing score?
The minimum passing score is 450 on ISACA’s 200–800 scaled range. It is not a raw percentage and should not be converted into 45% or 56.25%.
Can I take the CISM exam online from Oman?
ISACA currently supports remotely proctored examinations as well as authorised PSI test centres. Confirm the options shown in your account and the current technical requirements before booking.
How long is CISM exam eligibility valid?
Current exam eligibility is six months from registration. One six-month extension is currently available for US$75, subject to the candidate-guide conditions.
How quickly are CISM results released?
A preliminary result is shown after completion. ISACA currently emails and posts the official result within ten working days.
What happens if I do not pass?
Current waiting periods are 30 days before attempt two, 90 days before attempt three and 90 days before attempt four. Four attempts are allowed within a rolling 12-month period, and each attempt requires the full registration fee.
How much does the CISM exam cost?
The current reference is US$575 for ISACA members and US$760 for non-members. The separate certification-application fee is currently US$50. These official costs are separate from EduDelphi tuition.
What is included in EduDelphi’s CISM course?
The course includes 40+ guided live hours, 3,000+ CISM questions, multiple full mocks and exam simulations, recordings, LMS access, notes, mind maps, flashcards, quick-reference resources, study plans, individual support, mock analysis, weak-area review and end-to-end candidate guidance.
How long does CISM preparation take?
There is no single preparation period for every candidate. A practical plan depends on existing security-management exposure, target test date, weekly availability and diagnostic performance. EduDelphi builds the plan around these factors rather than promising an unrealistic universal timeline.
Can I prepare while working full-time?
Yes. Flexible weekday, weekend and fast-track batches, complete recordings, self-paced reinforcement and structured revision are designed around working professionals.
Do you offer classroom and live-online CISM training?
Yes. Classroom, hybrid, live-online, private, self-paced and corporate routes are available. Current batch options should be requested for the preferred schedule.
Do you provide Arabic or bilingual support?
Arabic or bilingual teaching support can be discussed for the selected batch or corporate programme. Confirm current faculty and schedule availability before enrolment.
What is the difference between CISM and CISA?
CISM focuses on security governance, risk, programme and incident management. CISA focuses more strongly on information-systems audit, evidence, controls and assurance.
What is the difference between CISM and CISSP?
CISM is management- and governance-led. CISSP covers broader security architecture, engineering, operations and technical-security breadth. The better choice depends on the target role.
Is CISM the same as ISO/IEC 27001 training?
No. CISM is an individual professional certification focused on information-security management. ISO/IEC 27001 Lead Implementer training focuses on implementing an information security management system, while ISO/IEC 27001 Lead Auditor training focuses on auditing that system against the ISO standard. Professionals may use both depending on their responsibilities.
Which is better for risk: CISM or CRISC?
CISM covers risk as part of leading an overall information-security programme. CRISC goes deeper into enterprise IT risk identification, assessment, response and control design.
Do you help with registration and certification applications?
Yes. EduDelphi supports candidates with the exam process, scheduling, fee planning, study sequencing and certification-application guidance. ISACA retains final control over all official decisions.
Do you offer corporate CISM training in Oman?
Yes. Private onsite and virtual programmes can include diagnostics, custom schedules, attendance tracking, progress visibility, domain readiness, mocks, manager summaries and organisation-relevant security cases.
How is CISM maintained after certification?
Current maintenance includes at least 20 CPE hours annually, 120 CPE hours over three years, annual maintenance fees, professional-ethics compliance and participation in an audit if selected.
Is this CISM the ISACA credential?
Yes. This page concerns ISACA’s Certified Information Security Manager certification and EduDelphi’s independent preparation course for it.
Get Your CISM Syllabus, Oman Fees and Exam-Date Plan
Tell us your role, experience, preferred schedule and intended exam month. We will help you compare the current course routes, understand the applicable 2026 outline and build a practical preparation path.
- Current Oman course fee and inclusions
- Weekday, weekend and fast-track batch options
- Live, classroom, hybrid, private and self-paced routes
- Correct exam-outline guidance for your test date
Request Current CISM Course Details
Receive the syllabus, fee guidance, current batch options and a preparation recommendation.
No artificial countdowns or pressure. Choose the route that fits your responsibilities and exam plan.
Certified Information Security Manager® and CISM® are trademarks of ISACA. EduDelphi provides independent exam preparation and candidate support; this does not imply endorsement by ISACA. Official requirements, fees and policies can change, so verify live details before registration.