Prepare for CISA with Teaching, Practice and Personal Support
Build your understanding of information-systems audit through 40+ live faculty-led hours, a resource-rich LMS, multiple mocks and clear trainer feedback. Study in a Singapore classroom, join live online or choose a private or supported self-paced route.
What is CISA? CISA stands for Certified Information Systems Auditor. It is ISACA’s professional certification for people who audit, assess and help govern information systems.
EduDelphi provides the teaching, practice and learner support. ISACA administers the examination and awards the certification after its requirements are met.
Explore our guide to CISA certification.
Your CISA Course at a Glance
- 40+ live faculty-led training hours
- All five current CISA exam domains
- Class recordings and organised LMS resources
- Topic questions, timed practice and multiple full mocks
- Individual mistake review and focused revision
- Notes, mind maps, infographics, checklists and AI study support
- Exam booking and certification-application guidance
- EduDelphi Certificate of Training
Live tuition is part of your preparation. Allow time for independent reading, practice and revision too.
Who Should Take This CISA Course?
CISA is a strong fit when your work involves technology audit, IT controls, assurance or technology risk.
IT auditors and assurance professionals: strengthen risk-based planning, control testing, evidence evaluation and reporting.
Internal auditors: build confidence when reviewing access, applications, systems changes, vendors and business continuity.
Technology-risk, compliance and IT professionals: understand how an auditor evaluates governance, security and control effectiveness.
You can prepare for the exam before completing the certification experience requirement. If you are newer to IT audit, we help you identify the foundation topics to study alongside the course.
What Is Included in Your CISA Course?
Clear teaching, useful resources and support that helps you understand mistakes, not just repeat questions.
Live Classes and Recordings
Learn with experienced faculty across all five domains. Revisit class recordings when a concept needs another look.
A Resource-Rich LMS
Study with organised notes, mind maps, infographics, summaries, glossaries, audit checklists and much more.
Questions and Multiple Mocks
Progress from topic questions to timed mixed practice and full-length mock exams, with clear answer explanations.
Trainer Feedback
Review mistakes, ask questions in live support and receive guidance on the concepts and decisions you need to improve.
AI Study Support
Use the LMS study assistant to clarify course concepts and find relevant resources. Your trainers remain available for deeper questions.
Exam and Study Guidance
Get help planning your preparation, understanding registration steps and preparing certification documents. Receive an EduDelphi training certificate.
Your CISA LMS and Study Resources
Your learning platform brings classes, resources, practice and revision together, so you know what to work on next.
Learn
Use live teaching, recordings, notes, visual summaries and AI study support to make difficult concepts easier to understand.
Practise
Work through topic questions, audit scenarios, timed tests and multiple mocks. Explanations show why the best answer is stronger than the alternatives.
Improve
Review domain performance and repeated mistakes. Discuss questions with faculty and use a focused revision plan to strengthen weaker areas.
Study planners, progress tracking, mistake review, revision checklists and further resources help keep your preparation organised.
CISA Syllabus and Exam Domain Weights
The current CISA framework became effective on 1 August 2024. It covers five domains; Domains 4 and 5 together account for 52% of the examination.
1. Information Systems Auditing Process — 18%
IS audit standards and ethics, risk-based audit planning, control considerations, audit project management, testing and sampling, evidence collection, data analytics, reporting and audit quality.
In class: practise defining an audit objective, choosing evidence and deciding the auditor’s most appropriate next action.
2. Governance and Management of IT — 18%
IT governance, strategy, organisational structures, policies, enterprise architecture, risk management, information security governance, privacy, resources, vendors and performance monitoring.
In class: distinguish control ownership from independent assurance and assess whether management has reliable oversight.
3. Information Systems Acquisition, Development and Implementation — 12%
Business cases, project governance, systems development, acquisition, testing, implementation, data conversion, release management and post-implementation review.
In class: evaluate testing, approvals and readiness before a system or change goes live.
4. Information Systems Operations and Business Resilience — 26%
IT service management, infrastructure and operations, asset management, interfaces, incidents, problems, change management, capacity, business impact analysis, continuity and disaster recovery.
In class: review recovery evidence, operational controls and the difference between a documented plan and a tested capability.
5. Protection of Information Assets — 26%
Security frameworks, physical and logical access, networks, endpoints, data protection, cryptography, security awareness, vulnerability management, monitoring and incident response.
In class: connect a security concern to the audit objective, control evidence and proportionate recommendation.
Source: ISACA CISA Exam Content Outline. For more detail, read our CISA exam format and domains guide.
Multiple Mocks and Personal Revision Support
Knowing the topic is only part of CISA preparation. You also need to recognise what the question is asking and choose the strongest audit response.
- Start with diagnostic and topic-level practice.
- Build confidence through mixed-domain and timed questions.
- Complete multiple full-length mocks using a four-hour exam rhythm.
- Review incorrect answers and plausible alternatives with faculty.
- Follow up on weaker concepts, question interpretation and pacing.
Live doubt-clearing and revision support help you keep improving after the main classes. Supported self-paced learners can also access faculty guidance.
See our CISA preparation guide for further study advice.
What Useful Feedback Looks Like
Illustrative trainer feedback: “You identified the relevant control, but your answer assumes it worked. Look for evidence from the review period before reaching a conclusion.”
The next step is targeted practice in evidence sufficiency and control testing, not simply another large set of unrelated questions.
Mock percentages help track preparation. They are not equivalent to ISACA’s official scaled score.
Singapore Classroom, Live Online and Private CISA Training
Choose the learning route that suits your background and work commitments. The focus stays on teaching, practice and support.
| Study option | Best suited to | What to expect |
|---|---|---|
| Singapore classroom | Professionals who prefer face-to-face learning | Faculty-led teaching, discussion and guided question practice |
| Live online | Learners who need to join from home or work | Interactive classes, recordings and LMS study resources |
| Supported self-paced | Learners who need greater study flexibility | Recorded teaching, LMS resources, practice and live faculty support |
| Private tuition | Learners seeking an individual preparation route | Teaching and revision focused on your learning needs |
| Focused revision | Experienced self-studiers and returning candidates | Mock review, question technique and weaker-topic support |
| Corporate cohorts | Audit, risk and technology teams | Private classroom, onsite, live online or blended programmes |
Our central Singapore teaching venue is at Raffles City Tower. Classroom and corporate arrangements can also be organised elsewhere across Singapore. Contact us to discuss the format and venue that work for you.
We build a study plan around your experience, target exam date and practice progress. Read our CISA study-duration guide for planning considerations.
CISA Exam Format and Certification Requirements
| Exam fact | Current position |
|---|---|
| Questions | 150 multiple-choice questions |
| Time | Four hours |
| Passing score | 450 on ISACA’s 200–800 scaled range |
| Delivery | PSI test centre or remote proctoring, subject to current availability and requirements |
| Results | Preliminary status after completion; official results generally within ten working days |
| Exam eligibility period | Six months from registration |
450 is a scaled score, not a raw percentage. There is no penalty for an incorrect answer, so candidates should answer every question.
Four hours across 150 questions averages about 96 seconds per question. This is a pacing illustration, not an ISACA-prescribed timing rule.
Exam Day and Scheduling
- No fixed exam season: registration is continuous.
- Six-month clock: take the exam within your registration eligibility period.
- 90-day scheduling horizon: appointments are shown up to 90 days ahead, subject to availability.
- 48-hour rescheduling rule: reschedule without penalty at least 48 hours before the appointment, within your eligibility period.
Before registering, check PSI availability in Singapore or the remote-testing requirements. Use the same name in MyISACA as on your accepted identification. Follow the current check-in instructions.
Source: ISACA Exam Candidate Guide.
You Can Take the CISA Exam Before You Have Five Years of Experience
There is no five-year experience requirement simply to sit the examination. The experience requirement applies to receiving the professional CISA certification. You have five years after passing to apply.
ISACA requires five years of qualifying information-systems audit, control, assurance or security experience. Permitted substitutions may reduce this requirement. Qualifying experience must fall within the ten years before your certification application.
CISA Experience-Waiver Planner
| Potential substitution | ISACA application treatment |
|---|---|
| General audit or general IS work | Up to 1 year |
| Associate degree | 1 year |
| Bachelor’s, master’s or doctorate in any field | 2 years |
| Master’s in Information Systems or a related field | 3 years |
| CIMA full certification | 2 years |
| ACCA member status | 2 years |
| Maximum substitutions combined | 3 years |
| Direct CISA-domain experience still required | Minimum 2 years |
Do not simply add every qualification together. ISACA’s substitution limits apply. General audit or IS work claimed as a waiver cannot overlap with the work dates claimed as direct CISA-domain experience.
Simple example: a qualifying bachelor’s degree may provide a two-year substitution, leaving three years of direct qualifying experience. An accepted three-year substitution still leaves at least two years of direct experience.
Final eligibility is determined by ISACA. EduDelphi can help you understand the application but cannot approve experience.
Source: ISACA CISA certification application and waiver rules.
How does CISA registration and certification work?
- Create or use your MyISACA account and register for the examination.
- Pay the official fee and choose an available PSI test-centre or remote appointment.
- Prepare, complete the examination and receive the official result.
- When you satisfy the requirements, submit the certification application and verified experience.
- Maintain the designation through continuing professional education and annual obligations.
Successful candidates must apply for certification within five years of passing. Qualifying experience must meet ISACA’s current recency rules.
Check ISACA’s current CISA guidance, our CISA requirements guide and certification application guide.
CISA Course Fees in Singapore
EduDelphi Tuition: Request an SGD Quote
Your quotation explains the selected study route, teaching, recordings, LMS resources, practice, mocks and trainer support. Instalment options are available.
Ask about full preparation, supported self-paced study, private tuition, revision or a corporate cohort.
EduDelphi tuition and official ISACA charges are separate.
Official ISACA Reference Fees
| Item | Member | Non-member |
|---|---|---|
| CISA exam | US$575 | US$760 |
| Certification application | US$50 | US$50 |
Reference checked October 2026. Verify current charges with ISACA before payment. Membership is not required simply to take the exam.
Plan Your Total CISA Cost
| Cost | Paid to | How to budget |
|---|---|---|
| EduDelphi tuition | EduDelphi | Request your SGD quote; instalments available |
| CISA exam | ISACA | US$575 member / US$760 non-member |
| Optional ISACA membership | ISACA | Check current membership and applicable chapter dues |
| Official QAE or review manual, if separately purchased | ISACA | Optional study purchase; check the selected product price |
| Certification application | ISACA | US$50 when applying after meeting the requirements |
| Annual maintenance after certification | ISACA | US$45 member / US$85 non-member per year |
Certified holders must also earn and report at least 20 CPE hours annually and 120 over three years. Annual certification maintenance is separate from membership dues.
Reference checked October 2026. See ISACA’s CISA maintenance requirements. Compare membership dues and benefits as well as the exam discount before choosing a buyer tier.
For a fuller breakdown, read our CISA exam-cost guide.
Meet Your CISA Trainers
Kashif Akhtar
Qualified Engineer | CSCP | PMP | CISA | CISM | CISSP | CRISC | CDPSE
30+ Years in Technology, IT Audit, Cyber Risk & Enterprise Systems | 13+ Years in Professional Certification Training
Kashif brings practical experience across technology, IT audit, cybersecurity, governance and enterprise systems in complex multinational environments.
For Singapore learners, he connects the five domains with banking, fintech, regional headquarters, technology firms, data centres and telecom. His sessions cover audit planning, governance, systems implementation, operations, continuity, access, cybersecurity and control assurance.
He is particularly strong at ISACA-style scenarios: identifying the best next auditor action, separating technical answers from audit-appropriate responses, and evaluating risk, evidence, ownership and control effectiveness.
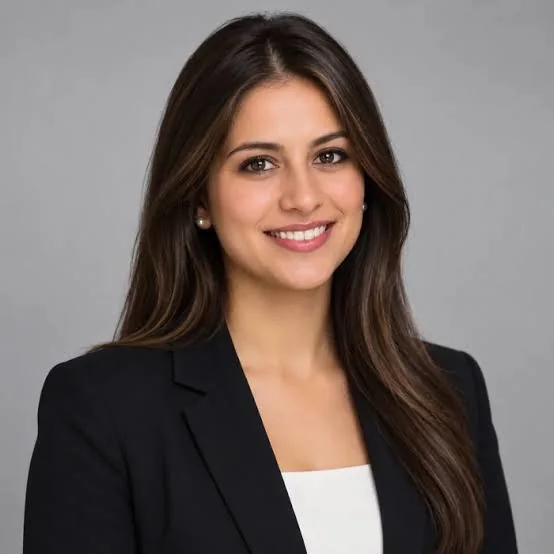
Tanvi P.
CISA | CIA | CFE | CAMS
20+ Years in Audit, Investigations, Controls and Regulatory Compliance
Former Regional Financial Crime Risk – Standard Chartered · Former Vice President, Citi Global Investigations Unit · Former KPMG Forensic Services Manager
Tanvi brings international experience across audit, investigations, controls, financial crime and compliance, with senior roles spanning major global institutions.
She adds the assurance and control-failure perspective, showing how weaknesses in access, systems, governance, data handling and monitoring can develop into larger operational or regulatory issues.
Her sessions focus on audit evidence, control evaluation, escalation, root causes and professional judgement, helping learners work through scenarios where several answers look plausible.
How CISA Skills Apply to Singapore Work
Singapore’s financial institutions, fintech businesses, regional headquarters and technology-dependent organisations need people who can assess controls and explain risk clearly.
| Work responsibility | CISA learning connection |
|---|---|
| Banking and fintech systems assurance | Access, change controls, audit evidence, governance and information-asset protection |
| Regional headquarters and shared services | ERP access, interfaces, vendor oversight and consistent control testing |
| Cloud and third-party assurance | Service responsibilities, assurance-report scope, customer controls and oversight |
| Business continuity and technology resilience | Business impact analysis, recovery testing and dependable operational evidence |
| Audit and advisory work | Risk-based scoping, testing, findings and management communication |
MAS’s Technology Risk Management Guidelines provide a useful local context for governance, systems, security and resilience. We use Singapore workplace examples to make the concepts practical; these examples do not replace or expand ISACA’s examinable syllabus.
Local reference: MAS Technology Risk Management Guidelines.
How do Singapore AI and cloud risks connect with this learning?
AI and cloud services raise familiar assurance questions: who owns the risk, which controls apply, what evidence is available, and how are third parties monitored? Singapore financial institutions also need to consider MAS’s current AI risk-management guidance. These examples help apply audit thinking to emerging services without presenting them as a new CISA examination domain.
Try an Original CISA Practice Question
Original EduDelphi mock question — not an actual ISACA exam question
An auditor is testing whether software releases received required approval and testing before deployment. Which procedure gives the strongest evidence that the control operated during the review period?
- Ask the change manager to confirm that the policy is followed.
- Review the policy and record that it requires approval.
- Select releases from the period and inspect their dated approval, testing and deployment records.
- Run a vulnerability scan on the production application.
View the answer and explanation
Best answer: C. It tests actual releases from the review period against the required control. Asking management is useful but is not sufficient evidence on its own. A policy shows how the control is designed, not whether it operated. A vulnerability scan addresses a different issue.
Our teaching approach: identify the objective, connect the risk to the control, choose relevant evidence and reach a supported conclusion.
In a Singapore regional finance-system example, we might also examine vendor-held access logs and leaver-account removal. A vendor’s security certificate does not automatically prove that your organisation’s access controls worked.
Corporate CISA Training in Singapore
Develop a shared approach to IT audit, controls and exam preparation across your audit, technology-risk or assurance team.
- Private CISA cohorts and team study plans
- Singapore onsite, classroom, live online and blended delivery
- Company-relevant audit and control scenarios
- Topic practice, multiple mocks and trainer feedback
- Progress reviews and targeted revision
- Custom schedules and programme coordination
Applied workshops can support teams that need practical control-testing, evidence and reporting skills alongside certification preparation.
CISA vs CIA, CISM, CRISC and Other Routes
| Route | Main focus | Choose it when |
|---|---|---|
| CISA | Information-systems audit and technology assurance | You evaluate systems, controls and audit evidence |
| CIA | Internal audit across business processes | You need a broader internal-audit pathway |
| CISM | Information-security management | You lead or manage a security programme |
| CRISC | Enterprise IT risk and controls | Your role centres on technology-risk decisions and control ownership |
| CISSP | Broad cybersecurity practice and architecture | You work across security design, implementation and operations |
| ISO 27001 Lead Auditor | Information-security management-system auditing | You need to audit an ISMS against ISO 27001 |
These routes can complement one another. For deeper comparisons, read CISA vs CISM, CIA vs CISA or CISA vs CISSP.
CISA Course Singapore FAQs
Can I take the CISA exam without five years of experience?
Yes. You can register for and take the exam before meeting the full certification experience requirement. Passing alone does not award the CISA designation. ISACA assesses the separate experience, substitution and application requirements.
Can I attend classroom CISA training in Singapore?
Yes. We offer Singapore classroom training alongside live online, private, supported self-paced and corporate options. Ask us about your preferred format and venue.
How many training hours are included?
The instructor-led route includes 40+ live faculty-led hours. You should also allow time for reading, practice, recordings, revision and mocks. Your overall study commitment depends on your background and progress.
Is ISACA membership compulsory to take CISA?
No. Membership is not compulsory simply to take the exam. Member and non-member examination fees differ, and membership has its own benefits and costs.
Is CISA suitable for an internal auditor without a technical background?
It can be, particularly if your role is expanding into systems assurance or IT controls. You may need more foundation study in technology concepts. We help you build a preparation plan around your existing knowledge.
Do supported self-paced learners receive trainer support?
Yes. Supported self-paced study combines recorded teaching, LMS resources and practice with faculty guidance. Focused revision is also available for candidates who have already studied the syllabus.
What happens if I do not pass the CISA exam?
ISACA currently allows up to four attempts in a rolling twelve-month period. The waiting period is 30 days after the first failed attempt and 90 days after the second and third. Each retake requires a new paid registration. We help you review mistakes and focus your revision before another attempt.
How do I keep CISA certification current?
Current maintenance requirements include at least 20 CPE hours each year and 120 across three years, plus annual fees and professional obligations. See ISACA’s maintenance guidance.
Can my employer sponsor my CISA course?
Yes. We can provide a quotation, syllabus, learning outcomes and enrolment documents for your employer’s approval or reimbursement process. Private company cohorts and corporate training are also available.
Can I use SkillsFuture Credit for this course?
SkillsFuture Credit eligibility depends on the specific approved course listing and your eligibility. Ask us to check the current position before relying on funding. Employer sponsorship is a separate option.
What certificate do I receive from EduDelphi?
You receive an EduDelphi Certificate of Training. The professional CISA certification is awarded separately by ISACA after its examination, experience and application requirements are met.
Which roles is CISA most relevant to in Singapore?
CISA is relevant to IT audit, technology assurance, IT controls, technology risk and some governance roles across financial institutions, audit firms and technology-dependent businesses. The best fit depends on your responsibilities, experience and career direction.
Official policies can change. Check the current ISACA CISA information before registration.
Get CISA Course Details and SGD Fees
Speak with us about the syllabus, classroom and online options, inclusions, instalments and a preparation plan that suits your background.
4.6/5 rating · 200+ EduDelphi Singapore reviews
EduDelphi Singapore250 N Bridge Rd, Raffles City Tower
Singapore 179101
Request CISA Course Details
Leave your name, email and phone number. Our team will help you choose the next step.